
The moment danger is detected, Linux isolates itself.
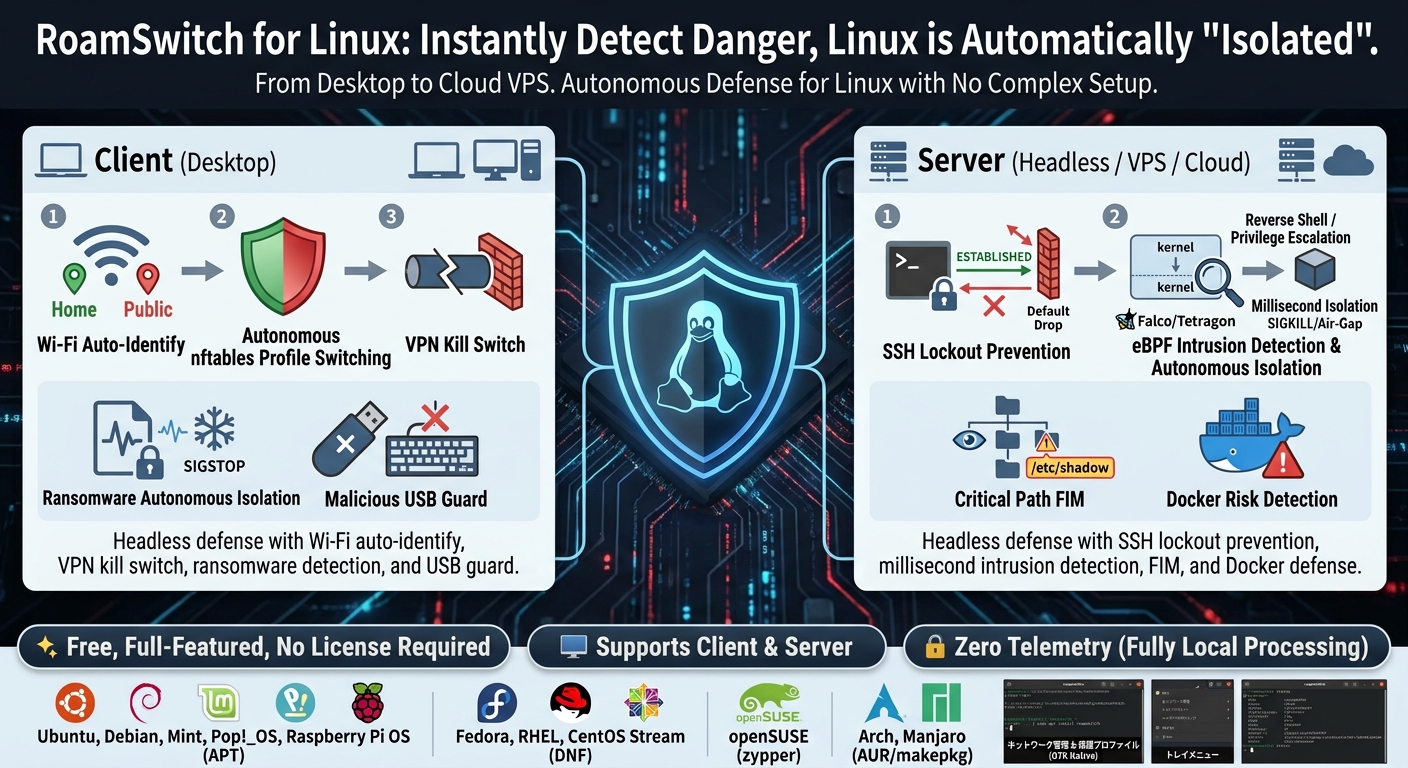
From desktop to cloud VPS, autonomous Linux defense with no complex setup. Client Edition: Wi-Fi auto-detection and a VPN kill-switch. Server Edition: SSH lockout prevention and millisecond intrusion detection. Both fully headless.
Install from your distribution
Adding the official repository lets updates flow through your normal update command and makes the in-app update check work. Select "Client Edition (Desktop)" or "Server Edition (Headless)" for your use case.
Ubuntu / Debian / Mint / Pop!_OS / Raspberry Pi OS (APT)
curl -fsSL https://lafine.net/apt/roamswitch-archive-keyring.asc \
  | sudo gpg --dearmor -o /usr/share/keyrings/roamswitch-archive-keyring.gpg
echo "deb [arch=amd64,arm64 signed-by=/usr/share/keyrings/roamswitch-archive-keyring.gpg] https://lafine.net/apt stable main" \
  | sudo tee /etc/apt/sources.list.d/roamswitch.list
sudo apt update && sudo apt install roamswitch
Fedora / RHEL / CentOS Stream (DNF)
sudo rpm --import https://lafine.net/rpm/RPM-GPG-KEY-roamswitch
sudo curl -fsSL -o /etc/yum.repos.d/roamswitch.repo https://lafine.net/rpm/fedora/roamswitch.repo
sudo dnf install roamswitch
openSUSE (zypper)
sudo rpm --import https://lafine.net/rpm/RPM-GPG-KEY-roamswitch
sudo zypper addrepo https://lafine.net/rpm/opensuse/roamswitch.repo
sudo zypper refresh && sudo zypper install roamswitch
Arch / Manjaro / EndeavourOS
Not published on the AUR. Build from the bundled PKGBUILD (the release tarball is verified against the signing key).
gpg --recv-keys 9C12964366B8547511AAEAF5773A9A39ECBD1537
curl -fsSLO https://lafine.net/linux/dl/PKGBUILD
curl -fsSLO https://lafine.net/linux/dl/roamswitch.install
makepkg -si
Without a repository, download signed tarballs (.tar.gz + .tar.gz.asc, amd64 / aarch64) directly from lafine.net/linux/dl (the in-app update check will not work in that case).
After installation, roamswitch.service starts automatically and the tray icon runs at login. An onboarding wizard (GTK) appears on first launch. The CLI (roamswitch status) prints diagnostics in Japanese or English depending on your OS locale.
Autonomous defense, running natively on Linux
🛡️ Autonomous nftables profile switchingClient Edition only
On trusted networks (home) it allows comfortable local traffic; at work it watches suspicious ports; on public Wi-Fi it stealth-drops all inbound. Decided by gateway MAC, switched in milliseconds.
🚨 Autonomous ransomware isolationClient Edition only
fanotify + Shannon entropy + YARA detect an encryption burst and freeze the offending process instantly with SIGSTOP, then emergency-cut all external traffic (Air-Gap) and sharing services.
📶 Wi-Fi encryption-strength warningClient Edition only
On Open / WEP / WPA networks it raises the protection level automatically with a desktop notification. Optional auto stop/restore of sharing services (SSH/Samba/RDP).
🔌 Unauthorized USB / BadUSB guardClient Edition only
An unapproved USB storage device is held for approval; a keystroke-injection device (a BadUSB keyboard) has its input suppressed in software via evdev — never a kernel-level port cutoff. Bundles ClamAV auto-scan and quarantine for the Downloads folder.
📜 24/30-item security audit
Scores 24 client items — LUKS, Secure Boot, LSM, SSH/sudo, sysctl, ARP pinning, exposed ports, browser Safe Browsing and more — or 30 CIS-Benchmark items on the Server Edition, in all 10 languages. Available from the GUI, the CLI and MCP.
🤖 Bundled MCP server
roamswitch-mcp lets AI agents such as Claude read the security state over JSON-RPC (stdio). Read-only and fully local. See MCP setup.
🔒 VPN tunnel + kill-switchClient Edition only
On public Wi-Fi, route all traffic through an encrypted WireGuard or Tailscale (exit-node) tunnel. An nftables kill-switch drops any clear-text leak outside the tunnel and never fails open if the tunnel drops. The primary man-in-the-middle defense.
🎣 Passive link guard (blocks phishing connections)Client Edition only
Reads the destination hostname of outbound connections from the DNS question, the TLS SNI and the HTTP Host header, and warns about or blocks connections to phishing / scam sites (block by default, and it works even for DoH browsers). In warn mode a no-answer is fail-closed. Verdicts use a local feed plus offline heuristics only; the destination is never sent anywhere.
🖧 Autonomous Server Defense & SSH Lockout PreventionServer Edition only
Applies inbound Default Drop automatically for cloud VPS and data center nodes. Actively preserves existing administrative SSH sessions (ESTABLISHED state) to prevent administrator lockout. An optional guard.yaml lets you fine-tune the containment action per severity, plus a safety timer that auto-restores isolation if nobody acknowledges it.
⚡ eBPF Threat Detection & Autonomous Isolation (Falco / Tetragon)
Captures kernel-level eBPF events (reverse shells, privilege escalations, unauthorized binary execution) over a UNIX socket in real time. Choose Falco (default) or Cilium Tetragon (gRPC) as the sensor. Instantly isolates compromised processes (SIGSTOP/SIGKILL) or hosts (Air-Gap) in milliseconds.
📂 Critical-Path FIM (File Integrity Monitoring)Server Edition only
Event-driven SHA-256 hash monitoring for critical system binaries and configurations including /etc/shadow, /etc/pam.d, and /usr/bin/ — tampering is detected the instant it happens (periodic scans remain as a backstop). Instantly flags backdoor installations and unauthorized tampering.
🧠 Resource Exhaustion / Process Anomaly GuardServer Edition only
Detects memory-leak DoS attacks and crash loops (a sign of a use-after-free exploit attempt). A healthy GC-backed runtime's normal sawtooth memory pattern is never mistaken for a leak; only sustained RSS growth with no recovery is flagged. Crash loops are recognized structurally from systemd's own fixed vocabulary (no new polling). Correlates with eBPF/FIM events by PID to assign a confidence tier (possible/correlated).
🧱 Egress / C2 Blocking & DNS SinkholeServer Edition only
Automatically blocks outbound connections to known-malicious IPs via a local threat feed. Optionally enable a DNS sinkhole (Quad9 / Cloudflare / AdGuard / CleanBrowsing) to also block malicious domain resolution (off by default so it never breaks internal DNS).
📢 Multi-Channel Emergency Incident AlertsServer Edition only
Dispatches detailed security incident telemetry to Slack, Discord, Microsoft Teams, Syslog, or custom Webhooks the millisecond a threat is intercepted, process killed, or host air-gapped.
🐳 Docker Risk Detection & Firewall Bypass Protection
Detects a privileged (--privileged) container or a docker.sock bind-mount the instant it starts, via docker events (notify-only). DOCKER-USER chain firewall-bypass protection runs at all times on both the client and server editions.
🧫 File Scan Guard (YARA + ClamAV)Server Edition only
Periodically scans directories that store files for others — a mail relay, a shared folder, an upload endpoint (an added layer for arbitrary shared directories, separate from the client edition's automatic Downloads-folder scan). The embedded YARA engine always runs with no external dependency; ClamAV can be added as an optional second opinion. Confirmed threats are quarantined automatically.
🔑 Secret & API Key Leak Scanner
Detects API keys (OpenAI, Anthropic, AWS, GitHub, Slack, Stripe, and more) and SSH private keys — not just in pasted text, but across an entire directory (.git and similar are skipped automatically). Available via the CLI, MCP, and the Python SDK; nothing is ever transmitted off the host.
📦 Package CVE Scan (dpkg/pacman/dnf/zypper + dependencies)Client Edition only
Checks installed OS packages and your project's dependencies (npm, PyPI, crates.io, and 4 more ecosystems) against a locally-held known-CVE map. No network activity at all.
🖥️ ClickFix Defense: Detects and Clears Malicious Commands on the ClipboardClient Edition only
Defends against "ClickFix" — a fake ad or CAPTCHA page that tells you to copy and paste a "verification code" that's actually a malicious command. Polls the clipboard via gtk::Clipboard (works transparently across both X11 and Wayland) and, the moment a known-malicious pattern is copied, clears it and warns you — catching it uniformly whether the paste destination is a terminal, the GNOME/KDE run dialog, or anywhere else.
🔔 Notification History (Past 7 Days)
Look back through the notifications RoamSwitch has sent instead of only catching them the moment they appear. Available from the CLI (roamswitch notifications), GUI, MCP (get_notification_history), and the Python SDK. Entries older than the retention window are pruned automatically.
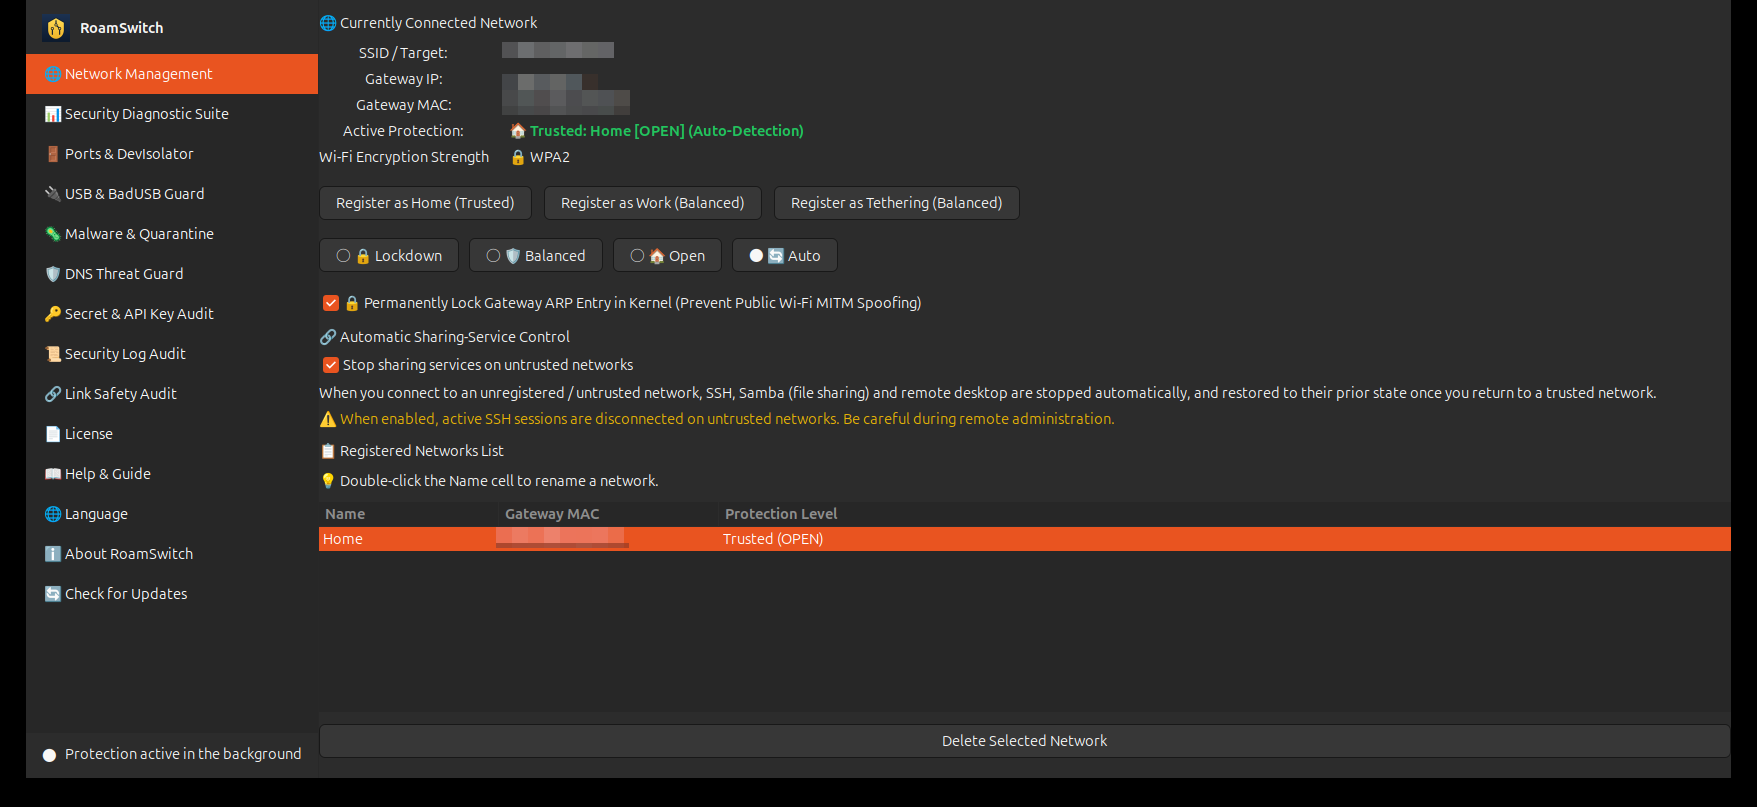
Identifies the connected gateway MAC and switches the nftables profile autonomously. Sharing-service control and ARP pinning live on this screen too.
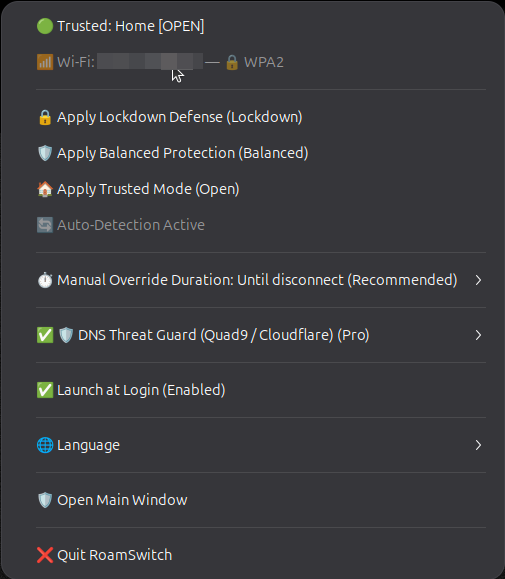
Switch protection level instantly, set the manual-override duration, toggle DNS threat protection and language — all from the tray.
Supported environments
| Fully supported | Ubuntu 22.04 / 24.04, Debian 12+, Linux Mint, Pop!_OS, elementary, Zorin, Raspberry Pi OS 64-bit (Bookworm), Ubuntu for Raspberry Pi |
|---|---|
| Architecture | x86_64 / aarch64 (Raspberry Pi 4 / 5, AWS Graviton, etc.) |
| Required | systemd, nftables. The Client Edition's tray UI needs an AppIndicator/StatusNotifierItem desktop (KDE / Cinnamon / MATE / Budgie, or GNOME with the extension). The Server Edition runs fully headless. |
| Packages | APT (Ubuntu/Debian family), DNF (Fedora/RHEL/Rocky/Alma), zypper (openSUSE), AUR (Arch). Non-systemd distros (Alpine / Void / Devuan) are not supported. |
| Use case | We ship two packages: a Client Edition (GUI + tray) for workstations and laptops, and a Server Edition (headless, Default Drop, eBPF/Falco integration) for cloud VPS, container hosts and data centers. |
Client Edition vs. Server Edition
The "Client Edition" for workstations and laptops, and the "Server Edition" for cloud VPS, container hosts and data centers — each tuned for autonomous defense in its own environment.
| Area | Client Edition (Desktop) | Server Edition (Headless) |
|---|---|---|
| Network detection & profile switching | Autonomous switching by Wi-Fi / gateway MAC (3 profiles) | Static policy (/etc/roamswitch/server.conf, fixed Default Drop) |
| Firewall posture | Auto-selects Open / Balanced / Lockdown | Default Drop + explicit allowlist of declared service ports + SSH lockout prevention |
| Outbound (egress) traffic | Passive link guard + DNS Threat Guard block phishing | Egress blocking of C2 / malicious domains + optional DNS sinkhole + emergency host Air-Gap isolation |
| VPN tunnel + kill-switch | ✅ WireGuard / Tailscale | ❌ Not available (management access is SSH-only; set up WireGuard or similar yourself via the OS if you need a VPN) |
| Ransomware, tampering & intrusion detection | fanotify autonomous ransomware detection & process freeze | eBPF intrusion detection (Falco / Tetragon) + critical-path FIM (event-driven, instant detection) + resource-exhaustion / crash-loop detection |
| Kernel hardening (sysctl / Yama / noexec) | Applied on an untrusted network | Always applied (bundled Docker-bypass protection filter) |
| Security health assessment | ✅ 24 items (GUI / CLI / MCP) | ✅ 30 items (CIS Benchmark, CLI / MCP) |
| Operator UI | GTK GUI + tray + CLI + MCP | CLI (roamswitch status --server / setup) + MCP + headless |
| Emergency notifications | Desktop notifications (GTK / libnotify) | Slack / Discord / Teams / Syslog / Webhook instant alerts |
| Central management & auditing | Added with a Business license | Added with a Business license (signed policy distribution, periodic check-in; free tier stays fully local) |
| Detailed documentation | Security Whitepaper (Client) → | Server Edition Operations Manual / Security Whitepaper (Linux Server) |
Server Edition Operations Manual Security Whitepaper (Linux Server) CLI / headless operations guide →
🏢 RoamSwitch Business (for organizations)
The Community Edition is free with every feature. To manage many Linux machines across an organisation, the paid Business tier adds the management layer below. The endpoint defence (nftables switching, ransomware isolation, USB guarding, DNS, assessment, MCP) is identical to Community — nothing is added or removed.
| What you can add | Summary |
|---|---|
| Fleet management | Enrol devices with an Ed25519-signed organisation token; aggregate protection level, health score and policy status via periodic check-in. |
| Signed bulk policy distribution | Distribute trusted networks, away level, sharing-service control and each guard's enforced value as Ed25519-signed JSON. Locked on the endpoint. |
| Signed private APT / RPM | A private repository signed with an organisation-specific GPG key. In-app update checks keep working. |
| SLA support | A contract-based contact for deployment design, policy design and incident response (Japanese, JST business days). |
Zero-Telemetry is kept — only devices the organisation has explicitly enrolled talk to a management server, and they send only the device ID, app version, health score, protection level and policy version. Mac Pro Lifetime owners get Business features free on their own Linux machines. Contact us for pricing and availability.
Contact us about Business🔒 Zero-Telemetry / License
Your traffic, connection history, browsed URLs and system logs are never sent anywhere. Update checks go only through your OS package manager (apt). RoamSwitch for Linux is proprietary freeware; the official distribution package (.deb) may be redistributed unmodified with all copyright notices intact. The source code is not published. Full text at /usr/share/doc/roamswitch/copyright. The RoamSwitchKit SDK is provided separately as open source.