
PersonalSOC
Centro operativo di sicurezza personale
PersonalSOC riunisce i log di questo dispositivo e lo stato delle sue difese in un rapporto che aiuta a individuare ogni anomalia. È un piccolo centro operativo di sicurezza (SOC) per chi non ha un team di sicurezza dedicato: capire la situazione del proprio dispositivo, prove alla mano, e decidere cosa fare dopo.
Viene fornito con il programma di installazione di RoamSwitch, ma è un'app separata con la propria icona. Funziona anche dove RoamSwitch non è installato.
Verifica dello stato con un clic
Premendo «Verifica lo stato» legge i log di questo dispositivo (a seconda del sistema: autenticazione SSH, auditd, web, DNS, log unificato di macOS), le impostazioni MCP e lo storico dei rilevamenti di RoamSwitch, tutto in sola lettura. Non eleva mai i privilegi; i log che non può leggere sono segnalati come non leggibili.
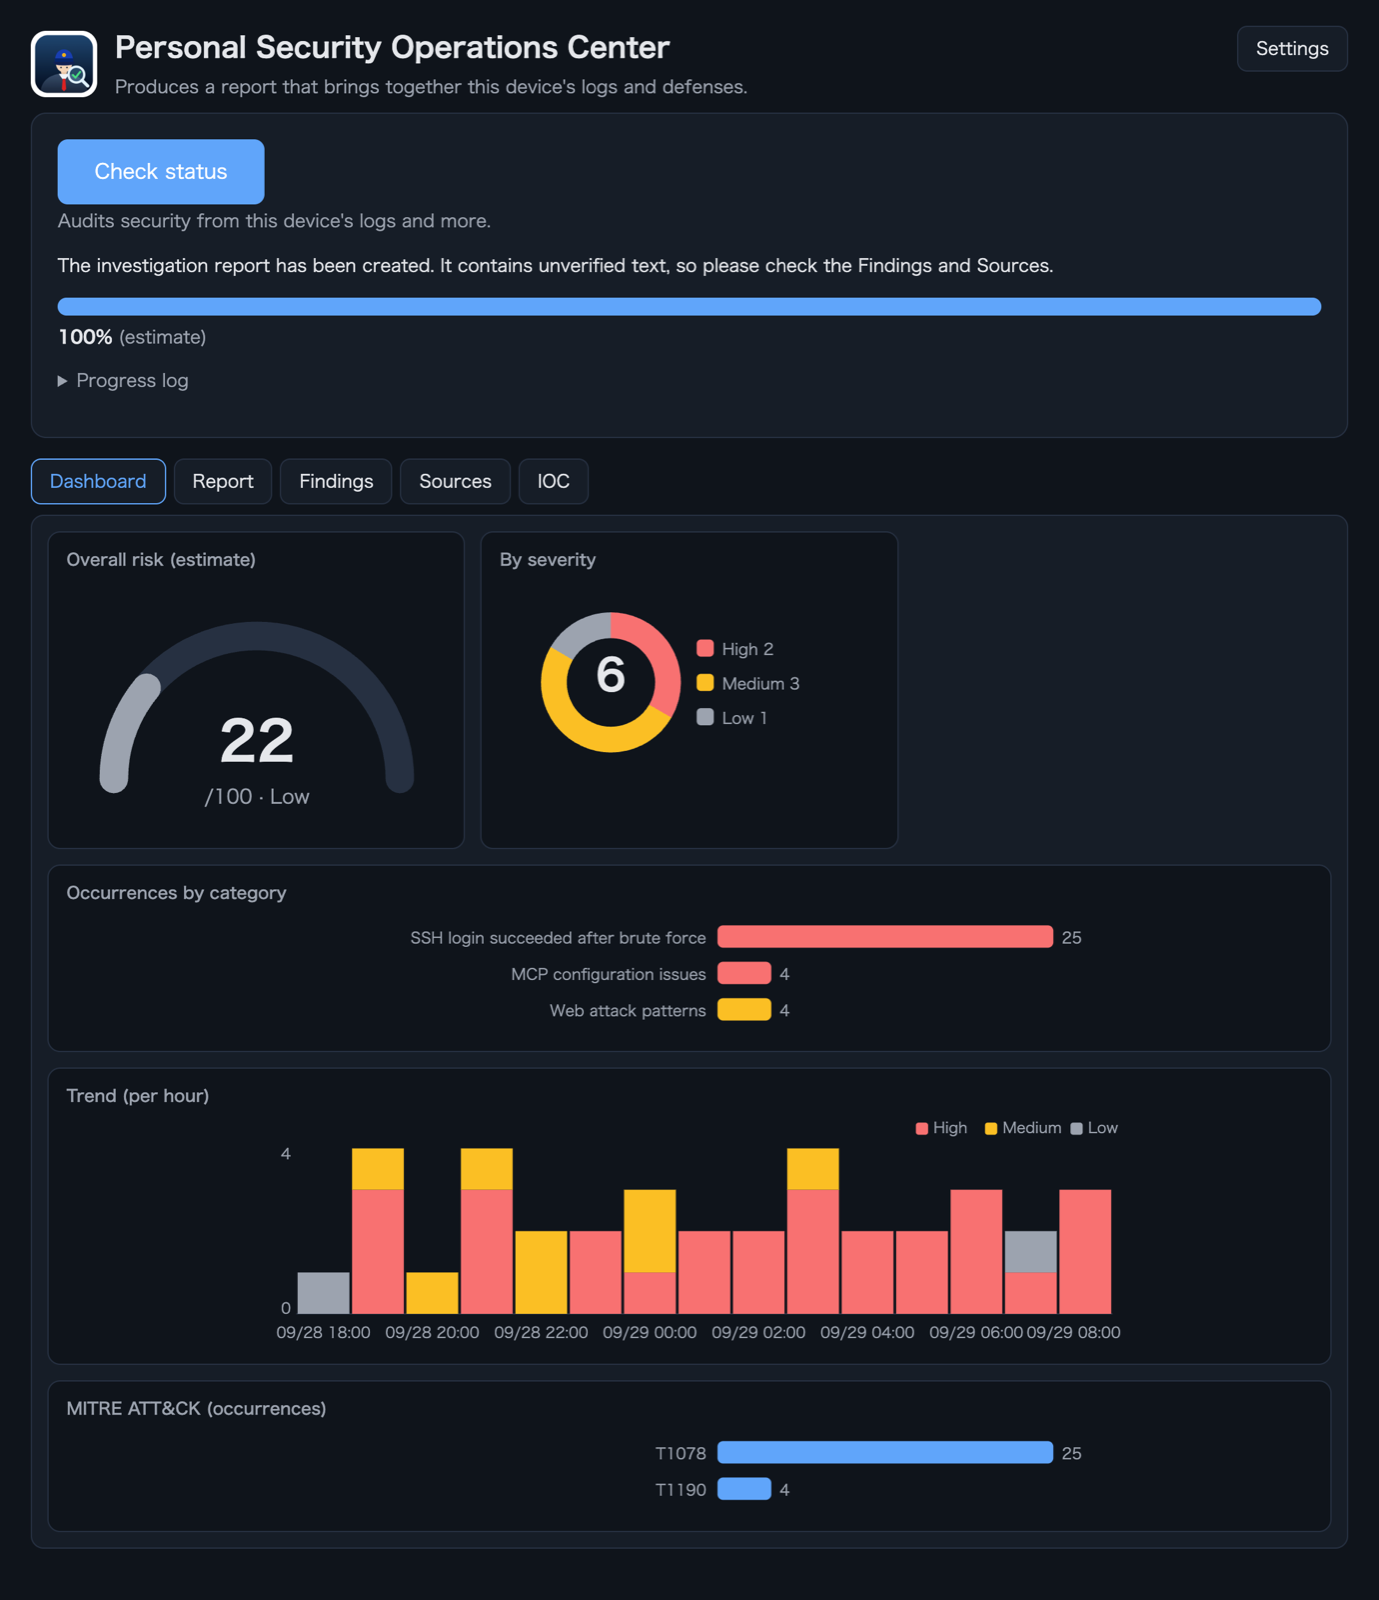
Dashboard
Rischio complessivo (stima), numero per gravità, occorrenze per categoria, andamento nel tempo e tecniche MITRE ATT&CK, a colpo d'occhio, in grafici.
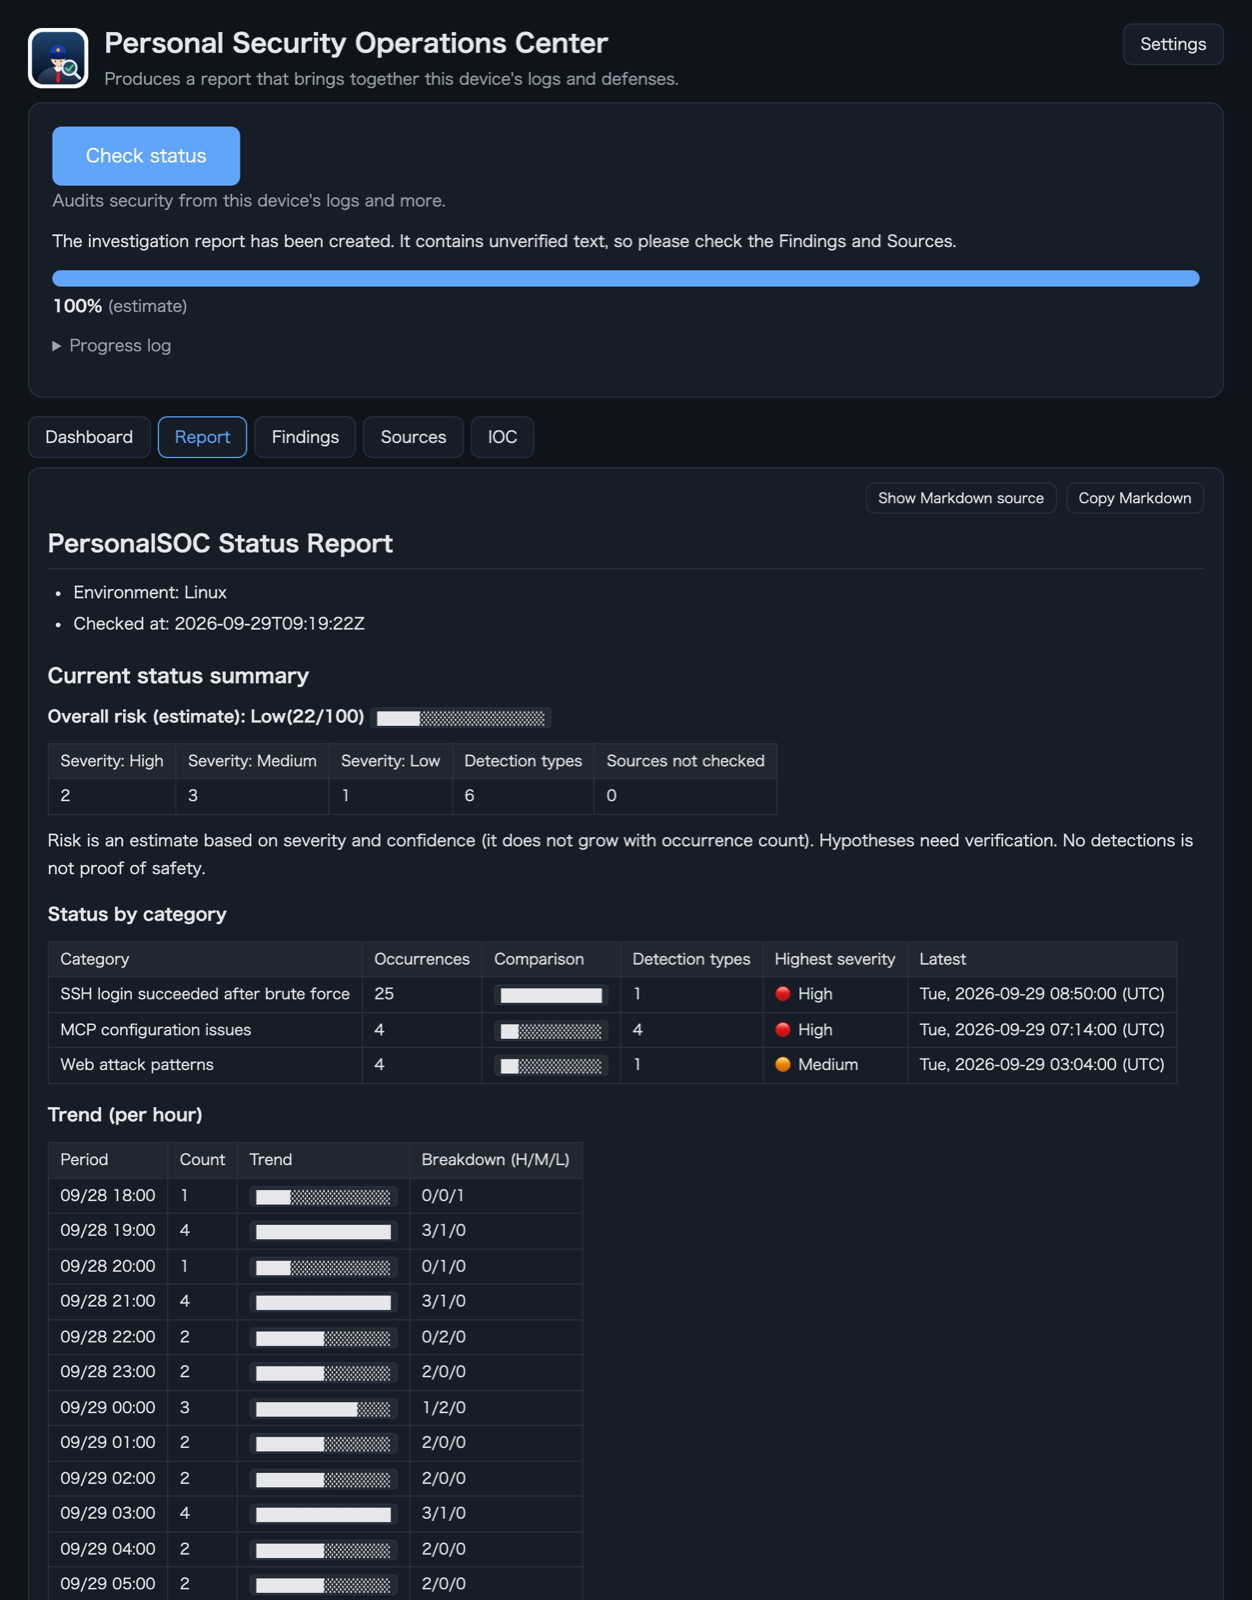
Rapporto
Fonti, risultati per categoria e IOC (in formato neutralizzato) sono raccolti in un rapporto Markdown. Gli orari sono mostrati nell'ora locale di questo dispositivo, in forma leggibile.
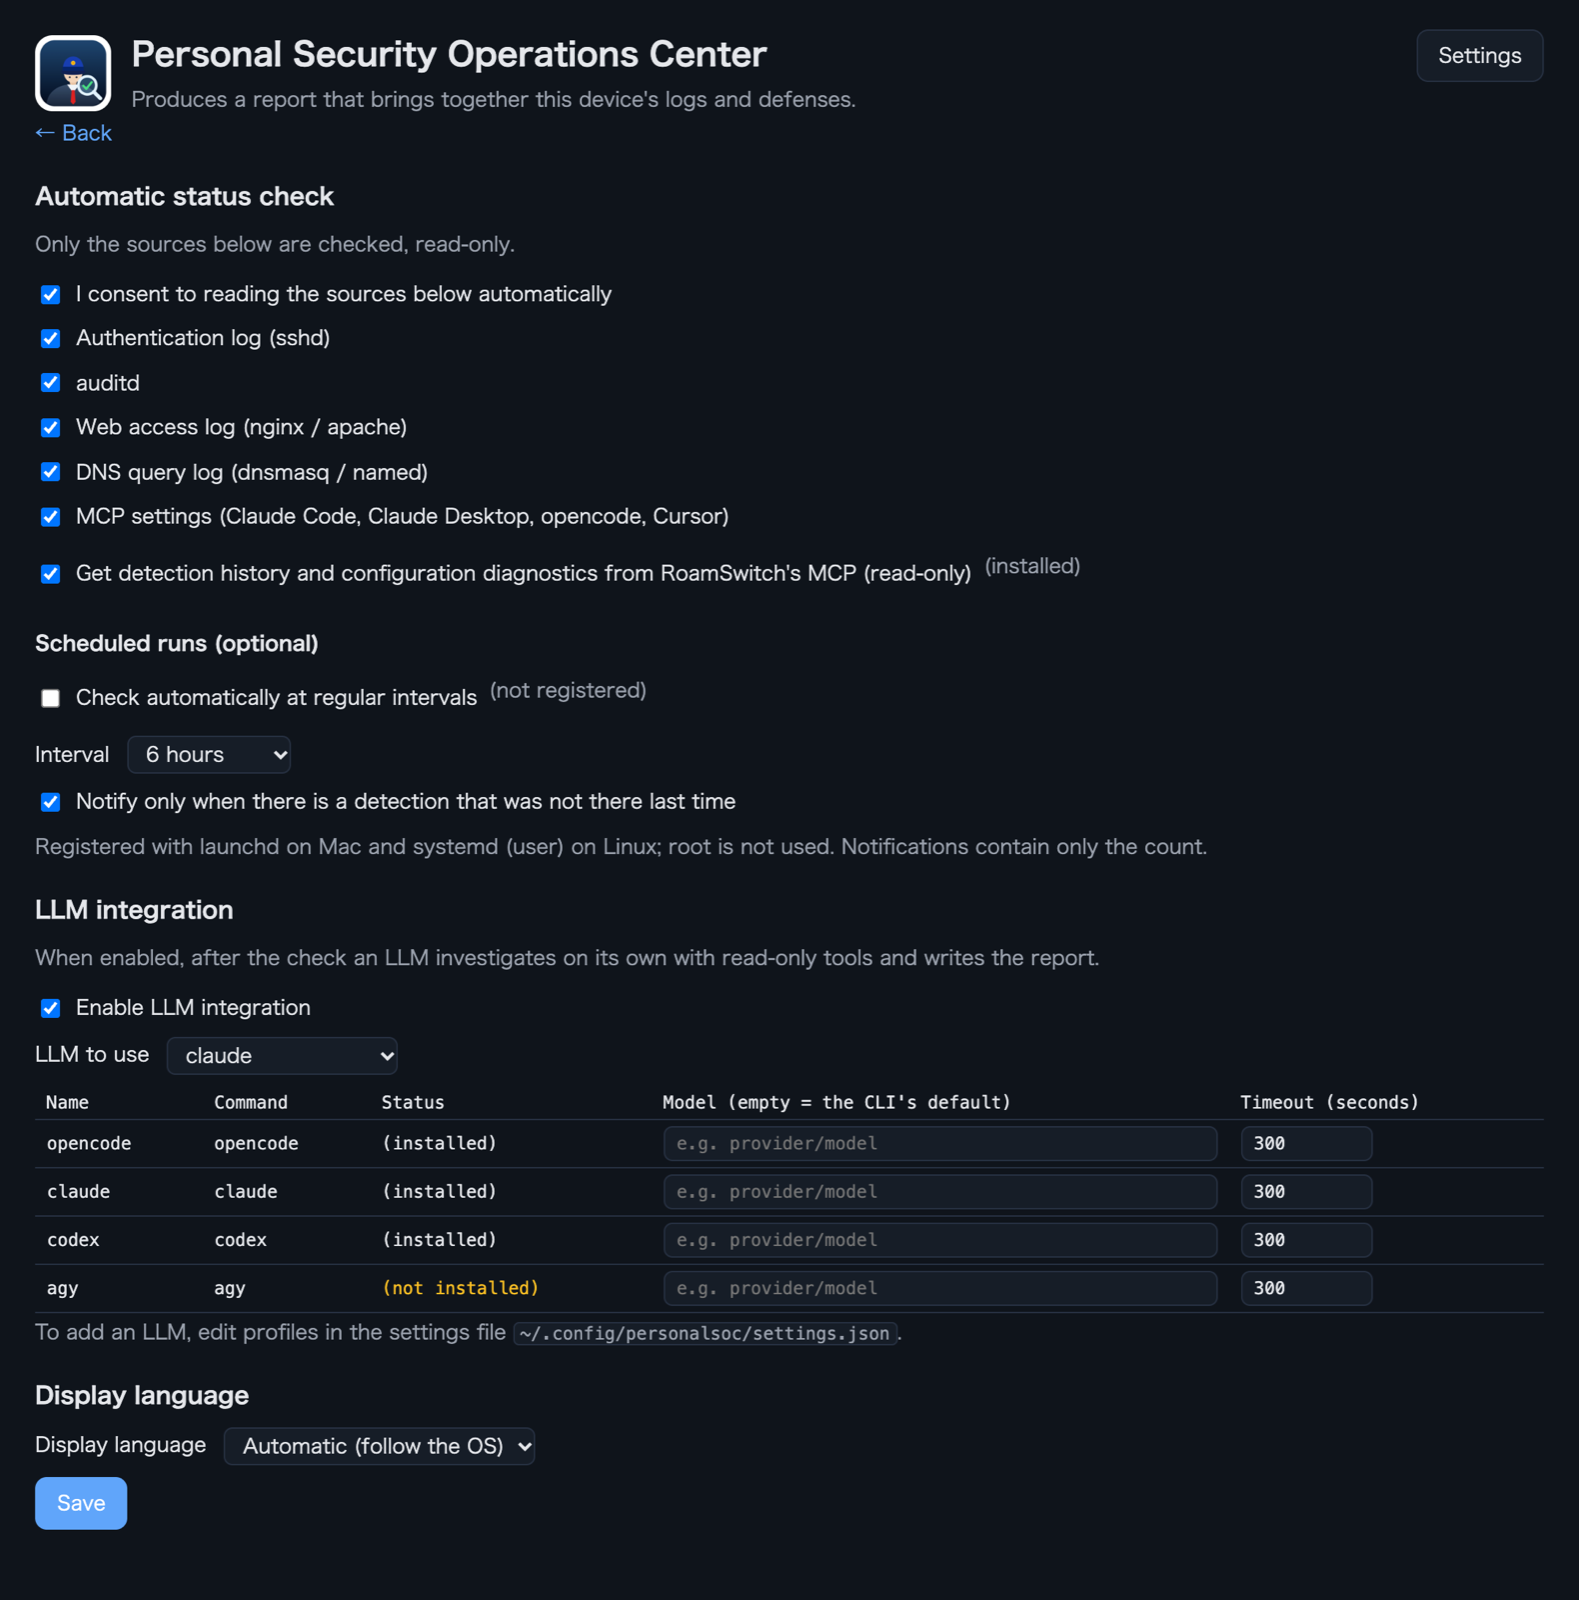
Indagine autonoma da parte di un LLM (facoltativa, disattivata per impostazione predefinita)
Se attivato, dopo la verifica un LLM indaga da solo e redige il rapporto come revisore. PersonalSOC gli dà solo strumenti di sola lettura consentiti, senza shell né file.
Esecuzione periodica (facoltativa)
Registrato con launchd su Mac e systemd (utente) su Linux, notifica solo quando c'è un rilevamento assente l'ultima volta (la notifica contiene solo il numero). Non si usa mai root.
10 lingue
Giapponese, inglese, tedesco, spagnolo, francese, italiano, coreano, portoghese e cinese semplificato e tradizionale. La lingua segue automaticamente quella del sistema.
Integrazione con l'MCP di RoamSwitch
Se RoamSwitch è installato, PersonalSOC ottiene dal server MCP di RoamSwitch (sola lettura) i rilevamenti non risolti e le diagnosi di configurazione non superate, e li riunisce con i risultati dei log in un unico rapporto. I rilevamenti identici vengono uniti in uno solo, con il conteggio e l'ora più recente. Anche durante l'indagine dell'LLM può richiamare solo gli strumenti di sola lettura di RoamSwitch; quelli che agiscono, come run_*, vengono rifiutati. Senza RoamSwitch questa fonte viene semplicemente saltata e si può disattivare nelle impostazioni.
Esempi di schermate
Tutti i dati mostrati in queste schermate, come gli indirizzi IP, sono fittizi.
Esempio di rapporto
Un esempio del rapporto (con l'integrazione LLM attiva). Si può copiare come Markdown e condividere così com'è.
PersonalSOC 状況報告書
- 環境: Linux
- 確認時刻: 2026-09-29T09:19:22Z
現在の状況サマリー
総合リスク(目安): 低(22/100) █████░░░░░░░░░░░░░░░
| 深刻度「高」 | 深刻度「中」 | 深刻度「低」 | 検知の種類 | 確認できなかった収集元 |
|---|---|---|---|---|
| 2 | 3 | 1 | 6 | 0 |
リスクは深刻度と確度による目安(発生件数では増えない)。仮説は要裏取り。検出なしは安全の証明ではない。
分類ごとの状況
| Categoria | 発生件数 | 件数の比較 | 検知の種類 | 最高の深刻度 | 最新 |
|---|---|---|---|---|---|
| SSH 総当たり後の認証成功 | 25 | ████████████ | 1 | 🔴 高 | 2026年9月29日(火) 08:50:00 (UTC+9) |
| MCP 設定の問題 | 4 | ██░░░░░░░░░░ | 4 | 🔴 高 | 2026年9月29日(火) 07:14:00 (UTC+9) |
| Web 攻撃パターン | 4 | ██░░░░░░░░░░ | 1 | 🟠 中 | 2026年9月29日(火) 03:04:00 (UTC+9) |
発生の推移(時間ごと)
| 時期 | 件数 | 推移 | 内訳(高/中/低) |
|---|---|---|---|
| 09/28 18:00 | 1 | ████░░░░░░░░░░░░ | 0/0/1 |
| 09/28 19:00 | 4 | ████████████████ | 3/1/0 |
| 09/28 20:00 | 1 | ████░░░░░░░░░░░░ | 0/1/0 |
| 09/28 21:00 | 4 | ████████████████ | 3/1/0 |
| 09/28 22:00 | 2 | ████████░░░░░░░░ | 0/2/0 |
| 09/28 23:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 00:00 | 3 | ████████████░░░░ | 1/2/0 |
| 09/29 01:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 02:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 03:00 | 4 | ████████████████ | 3/1/0 |
| 09/29 04:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 05:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 06:00 | 3 | ████████████░░░░ | 3/0/0 |
| 09/29 07:00 | 2 | ████████░░░░░░░░ | 1/0/1 |
| 09/29 08:00 | 3 | ████████████░░░░ | 3/0/0 |
直近の出来事(新しい順)
| 時刻 | Categoria | 深刻度 | Descrizione |
|---|---|---|---|
| 2026年9月29日(火) 08:50:00 (UTC+9) | SSH 総当たり後の認証成功 | 🔴 高 | 203.0.113.45 から失敗 24 回の後に成功が 1 回。正規利用者の入力ミスの可能性もあるため、当該アカウント… |
| 2026年9月29日(火) 07:14:00 (UTC+9) | MCP 設定の問題 | 🟡 低 | -y により初回導入の確認が省かれている。 |
| 2026年9月29日(火) 05:57:00 (UTC+9) | MCP 設定の問題 | 🔴 高 | コマンドがシェルの -c 経由。引数の組み立て次第で任意コマンドが実行される。直接実行に変えること。 |
| 2026年9月29日(火) 03:04:00 (UTC+9) | Web 攻撃パターン | 🟠 中 | 198.51.100.7 から 4 件。種別: パストラバーサル/LFI、SQLインジェクション、機密ファイル探索。成功… |
| 2026年9月29日(火) 00:11:00 (UTC+9) | MCP 設定の問題 | 🟠 中 | npx が版を固定せずに取得して実行する。上流が乗っ取られると次回起動で悪性コードが動く |
| 2026年9月28日(月) 21:18:00 (UTC+9) | MCP 設定の問題 | 🟠 中 | 環境変数 API_TOKEN に値が直接書かれている |
MITRE ATT&CK
| 技術 | 発生件数 | 件数の比較 | 検知の種類 |
|---|---|---|---|
| T1078 | 1 | ████████████ | 1 |
| T1190 | 1 | ████████████ | 1 |
監査レポート
セキュリティ監査レポート
Riepilogo
- 侵害が確定したとは言えませんが、優先して確認すべき点が2つあります。
- SSHの総当たりの後に、同じ送信元(203.0.113.45)からログインが成功しています。 失敗が24回続いた後の成功で、パスワードが破られた可能性があります(確度: 有力)。
- Webサーバーに、パス走査とSQLインジェクションを試す要求があります。応答は404で、成功の証拠はありません(確度: 仮説)。
推奨する対応
adminアカウントのパスワードを変更し、ログイン履歴を確認する。- SSHのパスワード認証をやめ、公開鍵認証にする。
- MCPの設定にある秘密の直書きを、環境変数の参照に置き換える。
収集元
| 確認したもの | 状態 | 検出 | 備考 |
|---|---|---|---|
| 認証ログ(sshd) | 読めた | 1 | |
| auditd | 該当なし | 0 | この環境に該当するログがない |
| Web アクセスログ(nginx / apache) | 読めた | 1 | |
| DNS クエリログ(dnsmasq / named) | 該当なし | 0 | この環境に該当するログがない |
| MCP の設定(Claude Code・Claude Desktop・opencode・Cursor) | 読めた | 4 | |
| RoamSwitch(MCP、読み取り専用) | 読めた | 0 |
検出事項
SSH 総当たり後の認証成功(検知 1 種類・発生 25 件)
| 深刻度 | 確度 | ATT&CK | Descrizione | 件数 | 最新 |
|---|---|---|---|---|---|
| 🔴 高 | 有力 | T1078 | 203.0.113.45 から失敗 24 回の後に成功が 1 回。正規利用者の入力ミスの可能性もあるため、当該アカウントの直後の操作を確認すること。(根拠の行: 1, 2, 3, 4, 5, 6, 7, 8, 9, 10, 11, 12, 13, 14, 15, 16, 17, 18, 19, 20 ...) | 1 | 2026年9月29日(火) 08:50:00 (UTC+9) |
MCP 設定の問題(検知 4 種類・発生 4 件)
| 深刻度 | 確度 | ATT&CK | Descrizione | 件数 | 最新 |
|---|---|---|---|---|---|
| 🔴 高 | 有力 | - | コマンドがシェルの -c 経由。引数の組み立て次第で任意コマンドが実行される。直接実行に変えること。 | 1 | 2026年9月29日(火) 05:57:00 (UTC+9) |
| 🟠 中 | 確定 | - | npx が版を固定せずに取得して実行する。上流が乗っ取られると次回起動で悪性コードが動く(ラグプル)。版またはハッシュを固定すること。 | 1 | 2026年9月29日(火) 00:11:00 (UTC+9) |
| 🟠 中 | 有力 | - | 環境変数 API_TOKEN に値が直接書かれている(値は表示しない)。環境変数参照かキーチェーンに移すこと。 | 1 | 2026年9月28日(月) 21:18:00 (UTC+9) |
| 🟡 低 | 確定 | - | -y により初回導入の確認が省かれている。 | 1 | 2026年9月29日(火) 07:14:00 (UTC+9) |
Web 攻撃パターン(検知 1 種類・発生 4 件)
| 深刻度 | 確度 | ATT&CK | Descrizione | 件数 | 最新 |
|---|---|---|---|---|---|
| 🟠 中 | 有力 | T1190 | 198.51.100.7 から 4 件。種別: パストラバーサル/LFI、SQLインジェクション、機密ファイル探索。成功応答は観測されていない。(根拠の行: 1, 2, 4, 5) | 1 | 2026年9月29日(火) 03:04:00 (UTC+9) |
IOC(無害化表記)
- IP:
198[.]51[.]100[.]7 - IP:
203[.]0[.]113[.]45 - ドメイン:
malware[.]example
調査の経過
LLM が調べた理由と、PersonalSOC が実行したツール。
- 検出事項の一覧を確認する
list_findings
- SSHの成功ログインの根拠を確認する
get_evidence(1)
PersonalSOC Status Report
- Environment: Linux
- Checked at: 2026-09-29T09:19:22Z
Current status summary
Overall risk (estimate): Low(22/100) █████░░░░░░░░░░░░░░░
| Severity: High | Severity: Medium | Severity: Low | Detection types | Sources not checked |
|---|---|---|---|---|
| 2 | 3 | 1 | 6 | 0 |
Risk is an estimate based on severity and confidence (it does not grow with occurrence count). Hypotheses need verification. No detections is not proof of safety.
Status by category
| Category | Occurrences | Comparison | Detection types | Highest severity | Latest |
|---|---|---|---|---|---|
| SSH login succeeded after brute force | 25 | ████████████ | 1 | 🔴 High | Tue, 2026-09-29 08:50:00 (UTC) |
| MCP configuration issues | 4 | ██░░░░░░░░░░ | 4 | 🔴 High | Tue, 2026-09-29 07:14:00 (UTC) |
| Web attack patterns | 4 | ██░░░░░░░░░░ | 1 | 🟠 Medium | Tue, 2026-09-29 03:04:00 (UTC) |
Trend (per hour)
| Period | Count | Trend | Breakdown (H/M/L) |
|---|---|---|---|
| 09/28 18:00 | 1 | ████░░░░░░░░░░░░ | 0/0/1 |
| 09/28 19:00 | 4 | ████████████████ | 3/1/0 |
| 09/28 20:00 | 1 | ████░░░░░░░░░░░░ | 0/1/0 |
| 09/28 21:00 | 4 | ████████████████ | 3/1/0 |
| 09/28 22:00 | 2 | ████████░░░░░░░░ | 0/2/0 |
| 09/28 23:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 00:00 | 3 | ████████████░░░░ | 1/2/0 |
| 09/29 01:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 02:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 03:00 | 4 | ████████████████ | 3/1/0 |
| 09/29 04:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 05:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 06:00 | 3 | ████████████░░░░ | 3/0/0 |
| 09/29 07:00 | 2 | ████████░░░░░░░░ | 1/0/1 |
| 09/29 08:00 | 3 | ████████████░░░░ | 3/0/0 |
Recent events (newest first)
| Time | Category | Severity | Details |
|---|---|---|---|
| Tue, 2026-09-29 08:50:00 (UTC) | SSH login succeeded after brute force | 🔴 High | 1 success |
| Tue, 2026-09-29 07:14:00 (UTC) | MCP configuration issues | 🟡 Low | -y skips the confirmation for the first installation. |
| Tue, 2026-09-29 05:57:00 (UTC) | MCP configuration issues | 🔴 High | The command runs through a shell's -c. Depending on how argu… |
| Tue, 2026-09-29 03:04:00 (UTC) | Web attack patterns | 🟠 Medium | 4 request |
| Tue, 2026-09-29 00:11:00 (UTC) | MCP configuration issues | 🟠 Medium | npx fetches and runs the package without pinning a version. … |
| Mon, 2026-09-28 21:18:00 (UTC) | MCP configuration issues | 🟠 Medium | The environment variable API_TOKEN has its value written dir… |
MITRE ATT&CK
| Technique | Occurrences | Comparison | Detection types |
|---|---|---|---|
| T1078 | 1 | ████████████ | 1 |
| T1190 | 1 | ████████████ | 1 |
Audit report
Security audit report
Summary
- A compromise is not confirmed, but two points need attention first.
- A login succeeded from the same source (203.0.113.45) right after an SSH brute-force run. Success after 24 failures suggests the password may have been guessed (confidence: likely).
- The web server received path-traversal and SQL injection attempts. All returned 404, so there is no evidence of success (confidence: hypothesis).
Recommended actions
- Change the
adminpassword and review its login history.- Turn off SSH password authentication and use public keys.
- Replace the hardcoded secret in the MCP configuration with an environment variable reference.
Sources
| Checked item | Status | Found | Note |
|---|---|---|---|
| Authentication log (sshd) | Read | 1 | |
| auditd | Not present | 0 | No matching log in this environment |
| Web access log (nginx / apache) | Read | 1 | |
| DNS query log (dnsmasq / named) | Not present | 0 | No matching log in this environment |
| MCP settings (Claude Code, Claude Desktop, opencode, Cursor) | Read | 4 | |
| RoamSwitch (MCP, read-only) | Read | 0 |
Findings
SSH login succeeded after brute force (1 type(s), 25 occurrence(s))
| Severity | Confidence | ATT&CK | Details | Count | Latest |
|---|---|---|---|---|---|
| 🔴 High | Likely | T1078 | 1 success(es) after 24 failures from 203.0.113.45. It may be a legitimate user's typo, so check what the account did right afterwards.(evidence lines: 1, 2, 3, 4, 5, 6, 7, 8, 9, 10, 11, 12, 13, 14, 15, 16, 17, 18, 19, 20 ...) | 1 | Tue, 2026-09-29 08:50:00 (UTC) |
MCP configuration issues (4 type(s), 4 occurrence(s))
| Severity | Confidence | ATT&CK | Details | Count | Latest |
|---|---|---|---|---|---|
| 🔴 High | Likely | - | The command runs through a shell's -c. Depending on how arguments are assembled, arbitrary commands can run. Change it to run the program directly. | 1 | Tue, 2026-09-29 05:57:00 (UTC) |
| 🟠 Medium | Confirmed | - | npx fetches and runs the package without pinning a version. If the upstream is hijacked, malicious code runs at the next launch (rug pull). Pin the version or a hash. | 1 | Tue, 2026-09-29 00:11:00 (UTC) |
| 🟠 Medium | Likely | - | The environment variable API_TOKEN has its value written directly (the value is not shown). Move it to an environment reference or the keychain. | 1 | Mon, 2026-09-28 21:18:00 (UTC) |
| 🟡 Low | Confirmed | - | -y skips the confirmation for the first installation. | 1 | Tue, 2026-09-29 07:14:00 (UTC) |
Web attack patterns (1 type(s), 4 occurrence(s))
| Severity | Confidence | ATT&CK | Details | Count | Latest |
|---|---|---|---|---|---|
| 🟠 Medium | Likely | T1190 | 4 request(s) from 198.51.100.7. Types: Path traversal / LFI, SQL injection, Probing for sensitive files. No successful response was observed.(evidence lines: 1, 2, 4, 5) | 1 | Tue, 2026-09-29 03:04:00 (UTC) |
IOCs (defanged)
- IP:
198[.]51[.]100[.]7 - IP:
203[.]0[.]113[.]45 - Domain:
malware[.]example
Investigation trail
The reasons the LLM gave and the tools PersonalSOC ran.
- Review the list of findings
list_findings
- Check the evidence for the successful SSH login
get_evidence(1)
Gli indirizzi IP e i log mostrati sono tutti fittizi. I rapporti possono essere prodotti nella lingua di visualizzazione (10 lingue).
Come avviarlo
Mac: apri PersonalSOC nella cartella Applicazioni (ha una propria icona, diversa da quella di RoamSwitch).
Linux: apri PersonalSOC dal menu delle applicazioni (ha una propria icona). Da terminale, esegui personalsoc-app.
Riga di comando: personalsoc scan --report (rapporto), personalsoc scan --llm <nome> (il LLM indaga da solo).
Privacy e ambito
PersonalSOC analizza i log interamente su questo dispositivo. Non apre porte in ascolto e la sua finestra non carica siti esterni.
L'integrazione LLM è disattivata per impostazione predefinita. Se attivata, PersonalSOC avvia il comando LLM scelto (opencode, claude, codex, agy, ecc.) e gli passa i dettagli dei rilevamenti e le righe di log su cui si basano (i segreti come chiavi e token sono mascherati). A seconda delle impostazioni di quel comando, il contenuto può essere inviato a un servizio esterno. Destinazione e trattamento dipendono dal LLM scelto e dai termini del suo fornitore.
Lo «Zero-Telemetry» di RoamSwitch (non invia mai il tuo traffico né i tuoi log da nessuna parte) descrive RoamSwitch stesso. Le comunicazioni che avvengono quando attivi l'integrazione LLM di PersonalSOC non ne fanno parte. Con l'integrazione LLM disattivata, PersonalSOC non invia mai il contenuto dei tuoi log fuori dal dispositivo.
Licenza
PersonalSOC è concesso in licenza con la Apache License 2.0 e non rientra nel contratto di licenza (EULA) di RoamSwitch. Il testo della licenza, il NOTICE e l'elenco del software di terze parti incluso si trovano, su Mac, dentro l'app (PersonalSOC.app/Contents/Resources) e, su Linux, in /usr/share/licenses/personalsoc/.
Requisiti e aggiornamenti
macOS 12 o successivo. Su Linux richiede WebKitGTK 4.1 (libwebkit2gtk-4.1), che i pacchetti deb e rpm installano automaticamente; su Arch (AUR) installa webkit2gtk-4.1 come dipendenza facoltativa. Su Mac si può aggiornare dalle impostazioni, in «Aggiornamenti». Si connette solo quando si preme il pulsante e il file scaricato viene verificato con una firma prima di essere installato. Su Linux è incluso negli aggiornamenti dei pacchetti di RoamSwitch.