
PersonalSOC
Centro de operaciones de seguridad personal
PersonalSOC reúne los registros de este equipo y el estado de sus defensas en un informe que ayuda a detectar cualquier anomalía. Es un pequeño centro de operaciones de seguridad (SOC) para personas sin un equipo de seguridad dedicado: entender la situación de su equipo, con pruebas, y decidir qué hacer a continuación.
Se entrega con el instalador de RoamSwitch, pero es una app independiente con su propio icono. Funciona incluso donde RoamSwitch no está instalado.
Comprobar el estado con un botón
Al pulsar «Comprobar estado», lee los registros de este equipo (según el sistema: autenticación SSH, auditd, web, DNS, registro unificado de macOS), sus ajustes de MCP y el historial de detecciones de RoamSwitch, todo en solo lectura. Nunca eleva sus privilegios; los registros que no puede leer se indican como no legibles.
Panel
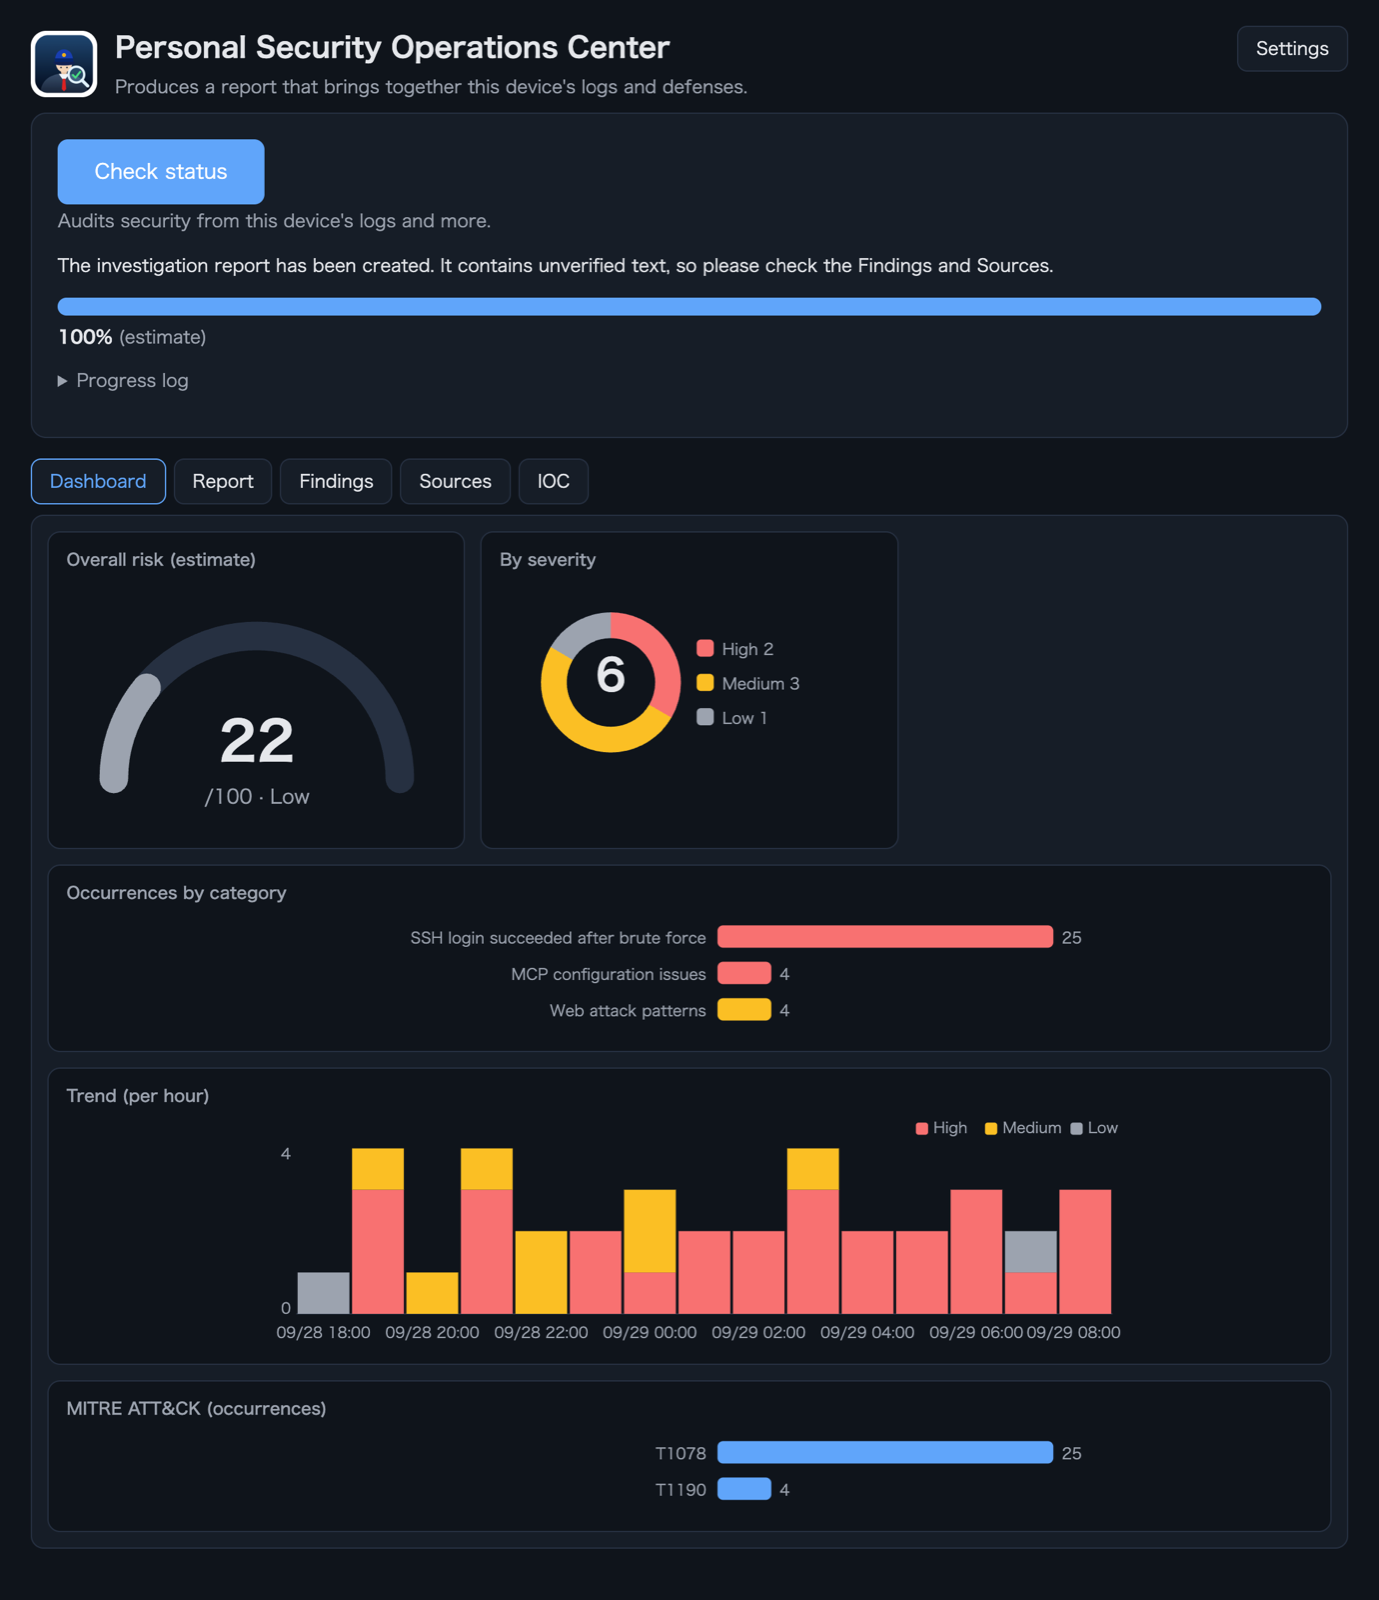
Vea de un vistazo el riesgo global (estimación), el número por gravedad, las apariciones por categoría, la evolución en el tiempo y las técnicas de MITRE ATT&CK, en gráficos.
Informe
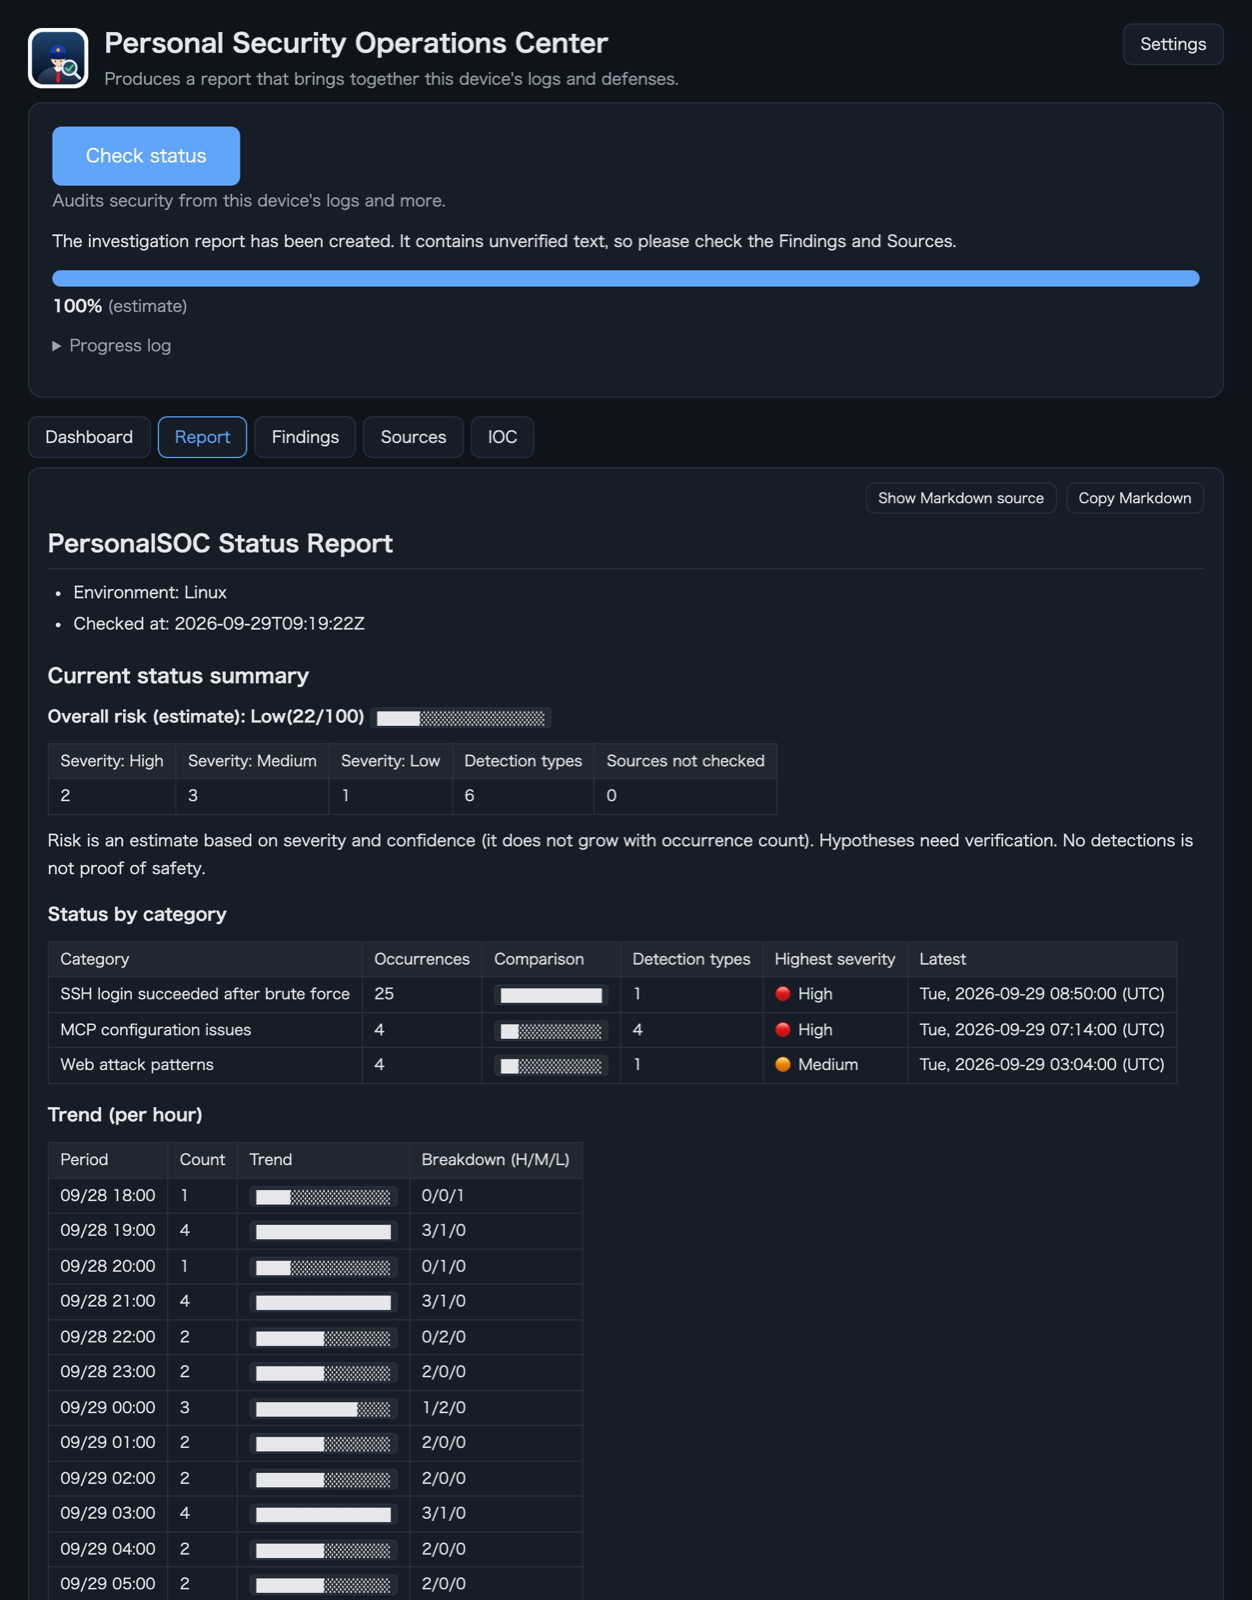
Las fuentes, los hallazgos por categoría y los IOC (en formato inofensivo) se reúnen en un informe Markdown. Las horas se muestran en la hora local de este equipo, en un formato legible.
Investigación autónoma por un LLM (opcional, desactivada por defecto)
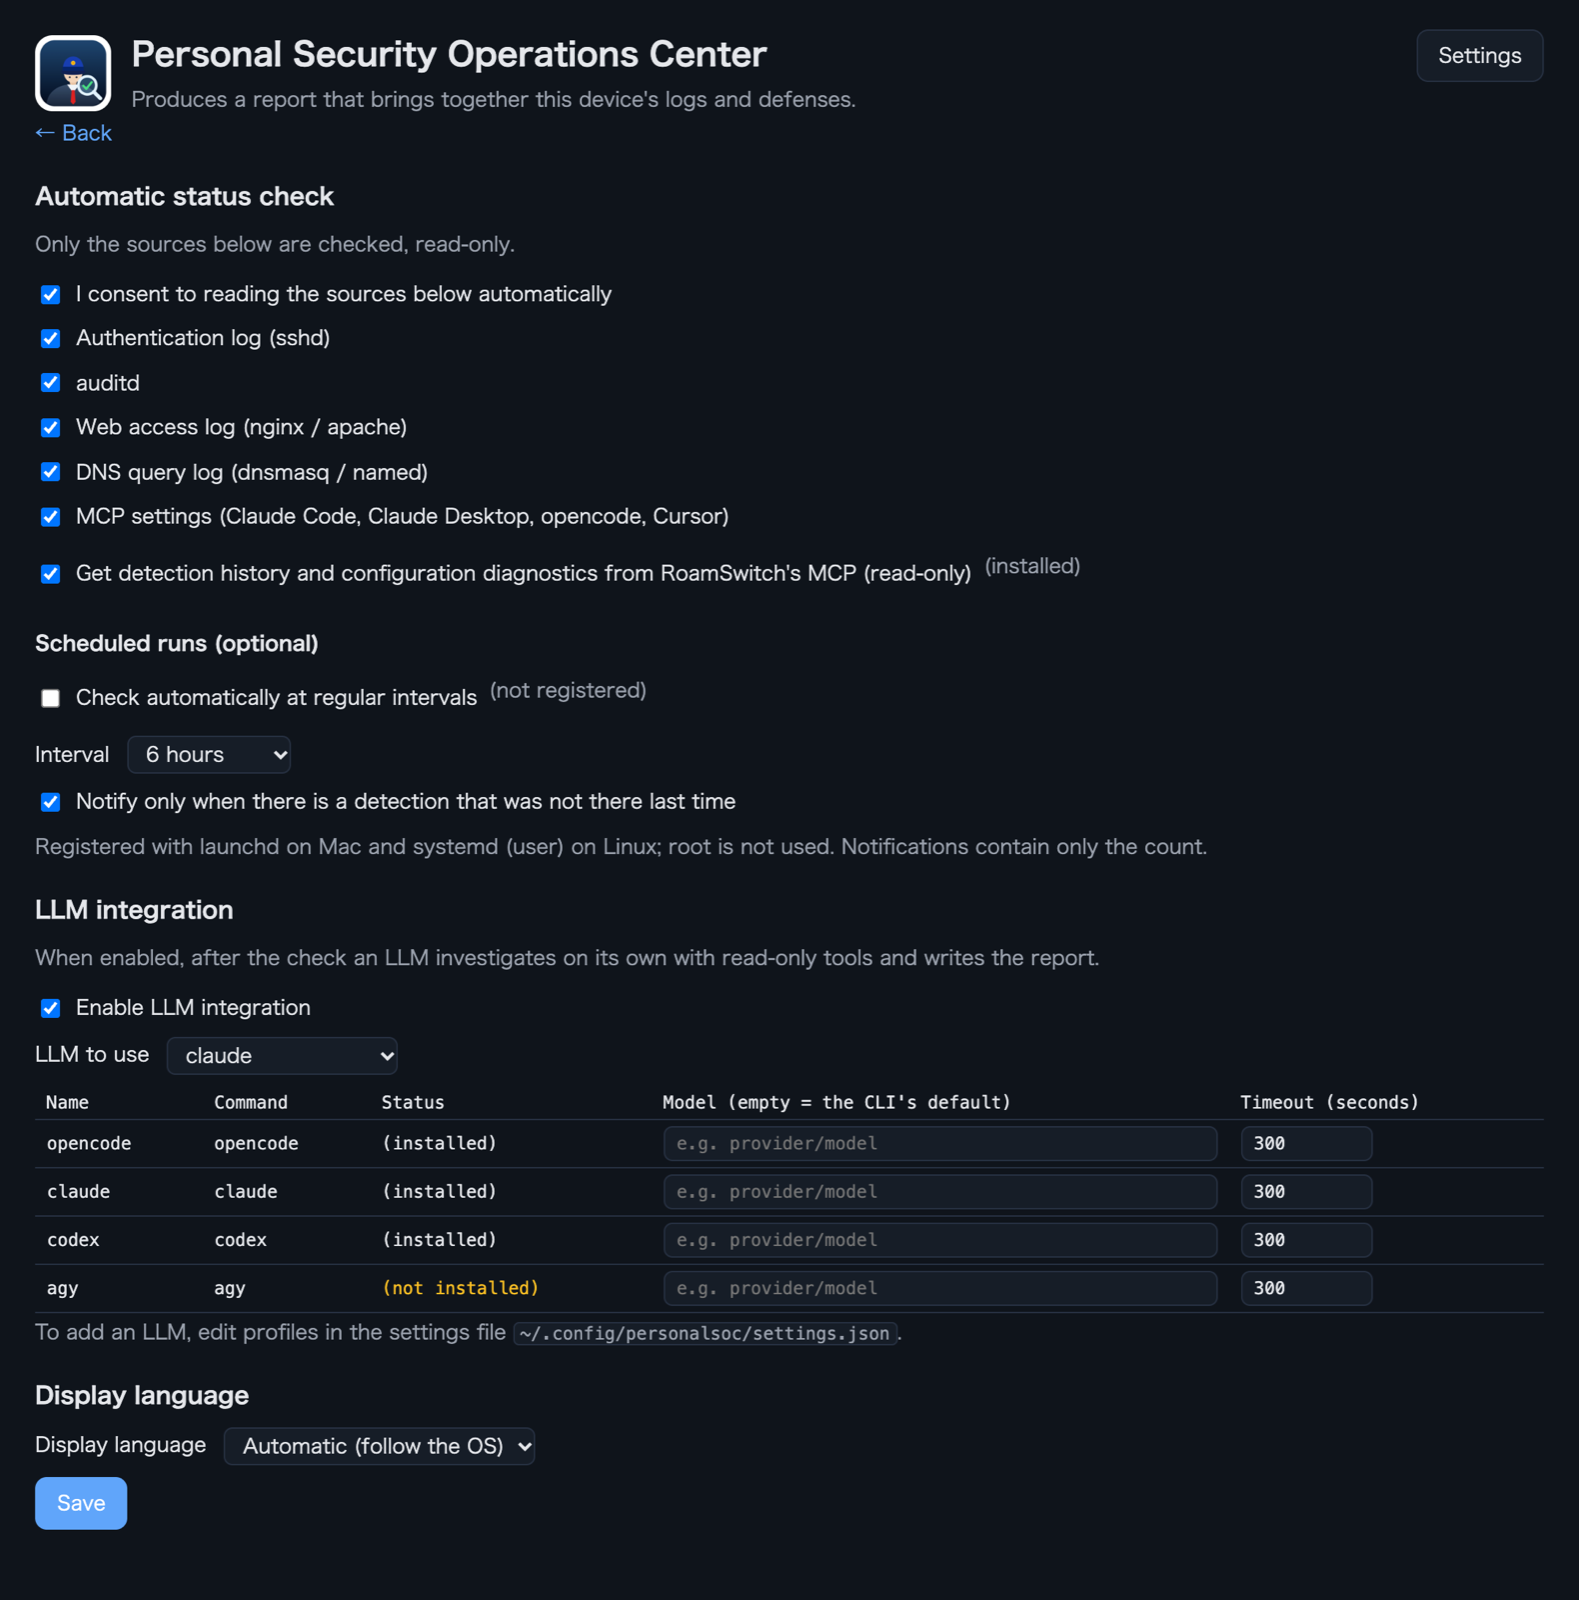
Si se activa, tras la comprobación un LLM investiga por sí mismo con herramientas de solo lectura y redacta el informe como auditor. El LLM solo puede solicitar herramientas de solo lectura permitidas; no puede tocar una shell ni archivos.
Ejecución periódica (opcional)
Se registra con launchd en Mac y con systemd (usuario) en Linux, y solo avisa cuando hay una detección que no estaba la última vez (la notificación solo contiene el número). No se usa root.
10 idiomas
Japonés, inglés, alemán, español, francés, italiano, coreano, portugués y chino simplificado y tradicional. El idioma sigue automáticamente al del sistema.
Integración con el MCP de RoamSwitch
Si RoamSwitch está instalado, PersonalSOC obtiene del servidor MCP de RoamSwitch (solo lectura) las detecciones sin resolver y los diagnósticos de configuración fallidos, y los reúne con los hallazgos de los registros en un único informe. Las detecciones idénticas se fusionan en una, con el recuento y la hora más reciente. En la investigación del LLM solo puede llamar a las herramientas de solo lectura de RoamSwitch; las que actúan, como run_*, se rechazan. Sin RoamSwitch, esta fuente simplemente se omite y también puede desactivarse en los ajustes.
Ejemplos de pantalla
Todos los datos de estas pantallas, como las direcciones IP, son ficticios.
Ejemplo de informe
Un ejemplo del informe (con la integración de LLM activada). Puede copiarlo como Markdown y compartirlo tal cual.
PersonalSOC 状況報告書
- 環境: Linux
- 確認時刻: 2026-09-29T09:19:22Z
現在の状況サマリー
総合リスク(目安): 低(22/100) █████░░░░░░░░░░░░░░░
| 深刻度「高」 | 深刻度「中」 | 深刻度「低」 | 検知の種類 | 確認できなかった収集元 |
|---|---|---|---|---|
| 2 | 3 | 1 | 6 | 0 |
リスクは深刻度と確度による目安(発生件数では増えない)。仮説は要裏取り。検出なしは安全の証明ではない。
分類ごとの状況
| Categoría | 発生件数 | 件数の比較 | 検知の種類 | 最高の深刻度 | 最新 |
|---|---|---|---|---|---|
| SSH 総当たり後の認証成功 | 25 | ████████████ | 1 | 🔴 高 | 2026年9月29日(火) 08:50:00 (UTC+9) |
| MCP 設定の問題 | 4 | ██░░░░░░░░░░ | 4 | 🔴 高 | 2026年9月29日(火) 07:14:00 (UTC+9) |
| Web 攻撃パターン | 4 | ██░░░░░░░░░░ | 1 | 🟠 中 | 2026年9月29日(火) 03:04:00 (UTC+9) |
発生の推移(時間ごと)
| 時期 | 件数 | 推移 | 内訳(高/中/低) |
|---|---|---|---|
| 09/28 18:00 | 1 | ████░░░░░░░░░░░░ | 0/0/1 |
| 09/28 19:00 | 4 | ████████████████ | 3/1/0 |
| 09/28 20:00 | 1 | ████░░░░░░░░░░░░ | 0/1/0 |
| 09/28 21:00 | 4 | ████████████████ | 3/1/0 |
| 09/28 22:00 | 2 | ████████░░░░░░░░ | 0/2/0 |
| 09/28 23:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 00:00 | 3 | ████████████░░░░ | 1/2/0 |
| 09/29 01:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 02:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 03:00 | 4 | ████████████████ | 3/1/0 |
| 09/29 04:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 05:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 06:00 | 3 | ████████████░░░░ | 3/0/0 |
| 09/29 07:00 | 2 | ████████░░░░░░░░ | 1/0/1 |
| 09/29 08:00 | 3 | ████████████░░░░ | 3/0/0 |
直近の出来事(新しい順)
| 時刻 | Categoría | 深刻度 | Descripción |
|---|---|---|---|
| 2026年9月29日(火) 08:50:00 (UTC+9) | SSH 総当たり後の認証成功 | 🔴 高 | 203.0.113.45 から失敗 24 回の後に成功が 1 回。正規利用者の入力ミスの可能性もあるため、当該アカウント… |
| 2026年9月29日(火) 07:14:00 (UTC+9) | MCP 設定の問題 | 🟡 低 | -y により初回導入の確認が省かれている。 |
| 2026年9月29日(火) 05:57:00 (UTC+9) | MCP 設定の問題 | 🔴 高 | コマンドがシェルの -c 経由。引数の組み立て次第で任意コマンドが実行される。直接実行に変えること。 |
| 2026年9月29日(火) 03:04:00 (UTC+9) | Web 攻撃パターン | 🟠 中 | 198.51.100.7 から 4 件。種別: パストラバーサル/LFI、SQLインジェクション、機密ファイル探索。成功… |
| 2026年9月29日(火) 00:11:00 (UTC+9) | MCP 設定の問題 | 🟠 中 | npx が版を固定せずに取得して実行する。上流が乗っ取られると次回起動で悪性コードが動く |
| 2026年9月28日(月) 21:18:00 (UTC+9) | MCP 設定の問題 | 🟠 中 | 環境変数 API_TOKEN に値が直接書かれている |
MITRE ATT&CK
| 技術 | 発生件数 | 件数の比較 | 検知の種類 |
|---|---|---|---|
| T1078 | 1 | ████████████ | 1 |
| T1190 | 1 | ████████████ | 1 |
監査レポート
セキュリティ監査レポート
Resumen
- 侵害が確定したとは言えませんが、優先して確認すべき点が2つあります。
- SSHの総当たりの後に、同じ送信元(203.0.113.45)からログインが成功しています。 失敗が24回続いた後の成功で、パスワードが破られた可能性があります(確度: 有力)。
- Webサーバーに、パス走査とSQLインジェクションを試す要求があります。応答は404で、成功の証拠はありません(確度: 仮説)。
推奨する対応
adminアカウントのパスワードを変更し、ログイン履歴を確認する。- SSHのパスワード認証をやめ、公開鍵認証にする。
- MCPの設定にある秘密の直書きを、環境変数の参照に置き換える。
収集元
| 確認したもの | 状態 | 検出 | 備考 |
|---|---|---|---|
| 認証ログ(sshd) | 読めた | 1 | |
| auditd | 該当なし | 0 | この環境に該当するログがない |
| Web アクセスログ(nginx / apache) | 読めた | 1 | |
| DNS クエリログ(dnsmasq / named) | 該当なし | 0 | この環境に該当するログがない |
| MCP の設定(Claude Code・Claude Desktop・opencode・Cursor) | 読めた | 4 | |
| RoamSwitch(MCP、読み取り専用) | 読めた | 0 |
検出事項
SSH 総当たり後の認証成功(検知 1 種類・発生 25 件)
| 深刻度 | 確度 | ATT&CK | Descripción | 件数 | 最新 |
|---|---|---|---|---|---|
| 🔴 高 | 有力 | T1078 | 203.0.113.45 から失敗 24 回の後に成功が 1 回。正規利用者の入力ミスの可能性もあるため、当該アカウントの直後の操作を確認すること。(根拠の行: 1, 2, 3, 4, 5, 6, 7, 8, 9, 10, 11, 12, 13, 14, 15, 16, 17, 18, 19, 20 ...) | 1 | 2026年9月29日(火) 08:50:00 (UTC+9) |
MCP 設定の問題(検知 4 種類・発生 4 件)
| 深刻度 | 確度 | ATT&CK | Descripción | 件数 | 最新 |
|---|---|---|---|---|---|
| 🔴 高 | 有力 | - | コマンドがシェルの -c 経由。引数の組み立て次第で任意コマンドが実行される。直接実行に変えること。 | 1 | 2026年9月29日(火) 05:57:00 (UTC+9) |
| 🟠 中 | 確定 | - | npx が版を固定せずに取得して実行する。上流が乗っ取られると次回起動で悪性コードが動く(ラグプル)。版またはハッシュを固定すること。 | 1 | 2026年9月29日(火) 00:11:00 (UTC+9) |
| 🟠 中 | 有力 | - | 環境変数 API_TOKEN に値が直接書かれている(値は表示しない)。環境変数参照かキーチェーンに移すこと。 | 1 | 2026年9月28日(月) 21:18:00 (UTC+9) |
| 🟡 低 | 確定 | - | -y により初回導入の確認が省かれている。 | 1 | 2026年9月29日(火) 07:14:00 (UTC+9) |
Web 攻撃パターン(検知 1 種類・発生 4 件)
| 深刻度 | 確度 | ATT&CK | Descripción | 件数 | 最新 |
|---|---|---|---|---|---|
| 🟠 中 | 有力 | T1190 | 198.51.100.7 から 4 件。種別: パストラバーサル/LFI、SQLインジェクション、機密ファイル探索。成功応答は観測されていない。(根拠の行: 1, 2, 4, 5) | 1 | 2026年9月29日(火) 03:04:00 (UTC+9) |
IOC(無害化表記)
- IP:
198[.]51[.]100[.]7 - IP:
203[.]0[.]113[.]45 - ドメイン:
malware[.]example
調査の経過
LLM が調べた理由と、PersonalSOC が実行したツール。
- 検出事項の一覧を確認する
list_findings
- SSHの成功ログインの根拠を確認する
get_evidence(1)
PersonalSOC Status Report
- Environment: Linux
- Checked at: 2026-09-29T09:19:22Z
Current status summary
Overall risk (estimate): Low(22/100) █████░░░░░░░░░░░░░░░
| Severity: High | Severity: Medium | Severity: Low | Detection types | Sources not checked |
|---|---|---|---|---|
| 2 | 3 | 1 | 6 | 0 |
Risk is an estimate based on severity and confidence (it does not grow with occurrence count). Hypotheses need verification. No detections is not proof of safety.
Status by category
| Category | Occurrences | Comparison | Detection types | Highest severity | Latest |
|---|---|---|---|---|---|
| SSH login succeeded after brute force | 25 | ████████████ | 1 | 🔴 High | Tue, 2026-09-29 08:50:00 (UTC) |
| MCP configuration issues | 4 | ██░░░░░░░░░░ | 4 | 🔴 High | Tue, 2026-09-29 07:14:00 (UTC) |
| Web attack patterns | 4 | ██░░░░░░░░░░ | 1 | 🟠 Medium | Tue, 2026-09-29 03:04:00 (UTC) |
Trend (per hour)
| Period | Count | Trend | Breakdown (H/M/L) |
|---|---|---|---|
| 09/28 18:00 | 1 | ████░░░░░░░░░░░░ | 0/0/1 |
| 09/28 19:00 | 4 | ████████████████ | 3/1/0 |
| 09/28 20:00 | 1 | ████░░░░░░░░░░░░ | 0/1/0 |
| 09/28 21:00 | 4 | ████████████████ | 3/1/0 |
| 09/28 22:00 | 2 | ████████░░░░░░░░ | 0/2/0 |
| 09/28 23:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 00:00 | 3 | ████████████░░░░ | 1/2/0 |
| 09/29 01:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 02:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 03:00 | 4 | ████████████████ | 3/1/0 |
| 09/29 04:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 05:00 | 2 | ████████░░░░░░░░ | 2/0/0 |
| 09/29 06:00 | 3 | ████████████░░░░ | 3/0/0 |
| 09/29 07:00 | 2 | ████████░░░░░░░░ | 1/0/1 |
| 09/29 08:00 | 3 | ████████████░░░░ | 3/0/0 |
Recent events (newest first)
| Time | Category | Severity | Details |
|---|---|---|---|
| Tue, 2026-09-29 08:50:00 (UTC) | SSH login succeeded after brute force | 🔴 High | 1 success |
| Tue, 2026-09-29 07:14:00 (UTC) | MCP configuration issues | 🟡 Low | -y skips the confirmation for the first installation. |
| Tue, 2026-09-29 05:57:00 (UTC) | MCP configuration issues | 🔴 High | The command runs through a shell's -c. Depending on how argu… |
| Tue, 2026-09-29 03:04:00 (UTC) | Web attack patterns | 🟠 Medium | 4 request |
| Tue, 2026-09-29 00:11:00 (UTC) | MCP configuration issues | 🟠 Medium | npx fetches and runs the package without pinning a version. … |
| Mon, 2026-09-28 21:18:00 (UTC) | MCP configuration issues | 🟠 Medium | The environment variable API_TOKEN has its value written dir… |
MITRE ATT&CK
| Technique | Occurrences | Comparison | Detection types |
|---|---|---|---|
| T1078 | 1 | ████████████ | 1 |
| T1190 | 1 | ████████████ | 1 |
Audit report
Security audit report
Summary
- A compromise is not confirmed, but two points need attention first.
- A login succeeded from the same source (203.0.113.45) right after an SSH brute-force run. Success after 24 failures suggests the password may have been guessed (confidence: likely).
- The web server received path-traversal and SQL injection attempts. All returned 404, so there is no evidence of success (confidence: hypothesis).
Recommended actions
- Change the
adminpassword and review its login history.- Turn off SSH password authentication and use public keys.
- Replace the hardcoded secret in the MCP configuration with an environment variable reference.
Sources
| Checked item | Status | Found | Note |
|---|---|---|---|
| Authentication log (sshd) | Read | 1 | |
| auditd | Not present | 0 | No matching log in this environment |
| Web access log (nginx / apache) | Read | 1 | |
| DNS query log (dnsmasq / named) | Not present | 0 | No matching log in this environment |
| MCP settings (Claude Code, Claude Desktop, opencode, Cursor) | Read | 4 | |
| RoamSwitch (MCP, read-only) | Read | 0 |
Findings
SSH login succeeded after brute force (1 type(s), 25 occurrence(s))
| Severity | Confidence | ATT&CK | Details | Count | Latest |
|---|---|---|---|---|---|
| 🔴 High | Likely | T1078 | 1 success(es) after 24 failures from 203.0.113.45. It may be a legitimate user's typo, so check what the account did right afterwards.(evidence lines: 1, 2, 3, 4, 5, 6, 7, 8, 9, 10, 11, 12, 13, 14, 15, 16, 17, 18, 19, 20 ...) | 1 | Tue, 2026-09-29 08:50:00 (UTC) |
MCP configuration issues (4 type(s), 4 occurrence(s))
| Severity | Confidence | ATT&CK | Details | Count | Latest |
|---|---|---|---|---|---|
| 🔴 High | Likely | - | The command runs through a shell's -c. Depending on how arguments are assembled, arbitrary commands can run. Change it to run the program directly. | 1 | Tue, 2026-09-29 05:57:00 (UTC) |
| 🟠 Medium | Confirmed | - | npx fetches and runs the package without pinning a version. If the upstream is hijacked, malicious code runs at the next launch (rug pull). Pin the version or a hash. | 1 | Tue, 2026-09-29 00:11:00 (UTC) |
| 🟠 Medium | Likely | - | The environment variable API_TOKEN has its value written directly (the value is not shown). Move it to an environment reference or the keychain. | 1 | Mon, 2026-09-28 21:18:00 (UTC) |
| 🟡 Low | Confirmed | - | -y skips the confirmation for the first installation. | 1 | Tue, 2026-09-29 07:14:00 (UTC) |
Web attack patterns (1 type(s), 4 occurrence(s))
| Severity | Confidence | ATT&CK | Details | Count | Latest |
|---|---|---|---|---|---|
| 🟠 Medium | Likely | T1190 | 4 request(s) from 198.51.100.7. Types: Path traversal / LFI, SQL injection, Probing for sensitive files. No successful response was observed.(evidence lines: 1, 2, 4, 5) | 1 | Tue, 2026-09-29 03:04:00 (UTC) |
IOCs (defanged)
- IP:
198[.]51[.]100[.]7 - IP:
203[.]0[.]113[.]45 - Domain:
malware[.]example
Investigation trail
The reasons the LLM gave and the tools PersonalSOC ran.
- Review the list of findings
list_findings
- Check the evidence for the successful SSH login
get_evidence(1)
Las direcciones IP y los registros mostrados son ficticios. Los informes pueden generarse en el idioma de visualización (10 idiomas).
Cómo abrirlo
Mac: abra PersonalSOC en la carpeta Aplicaciones (tiene su propio icono, distinto del de RoamSwitch).
Linux: abra PersonalSOC desde el menú de aplicaciones (tiene su propio icono). Desde una terminal, ejecute personalsoc-app.
Línea de comandos: personalsoc scan --report (informe), personalsoc scan --llm <nombre> (el LLM investiga por sí mismo).
Privacidad y alcance
PersonalSOC analiza los registros por completo en este equipo. No abre puertos a la escucha y su ventana no carga sitios externos.
La integración con LLM está desactivada por defecto. Al activarla, PersonalSOC inicia el comando de LLM que haya elegido (opencode, claude, codex, agy, etc.) y le pasa el detalle de las detecciones y las líneas de registro en que se basan (los secretos, como claves y tokens, se ocultan). Según los ajustes de ese comando, el contenido puede enviarse a un servicio externo. El destino y el tratamiento dependen del LLM elegido y de las condiciones de su proveedor.
El «Zero-Telemetry» de RoamSwitch (nunca envía su tráfico ni sus registros a ninguna parte) describe a RoamSwitch en sí. Las comunicaciones que se produzcan al activar la integración con LLM de PersonalSOC no están cubiertas. Con la integración con LLM desactivada, PersonalSOC nunca envía el contenido de sus registros fuera del equipo.
Licencia
PersonalSOC se licencia bajo la Apache License 2.0 y no está cubierto por el acuerdo de licencia (EULA) de RoamSwitch. El texto de la licencia, el NOTICE y la lista del software de terceros incluido están, en Mac, dentro de la app (PersonalSOC.app/Contents/Resources) y, en Linux, en /usr/share/licenses/personalsoc/.
Requisitos y actualizaciones
macOS 12 o posterior. En Linux necesita WebKitGTK 4.1 (libwebkit2gtk-4.1), que los paquetes deb y rpm instalan automáticamente; en Arch (AUR) instale webkit2gtk-4.1 como dependencia opcional. En Mac puede actualizar desde los ajustes, en «Actualizaciones». Solo se conecta al pulsar el botón, y el archivo descargado se verifica con una firma antes de instalarlo. En Linux se incluye en las actualizaciones de los paquetes de RoamSwitch.