
LAN에 두는 전용 센서 노드 “RoamSwitch Sensor”
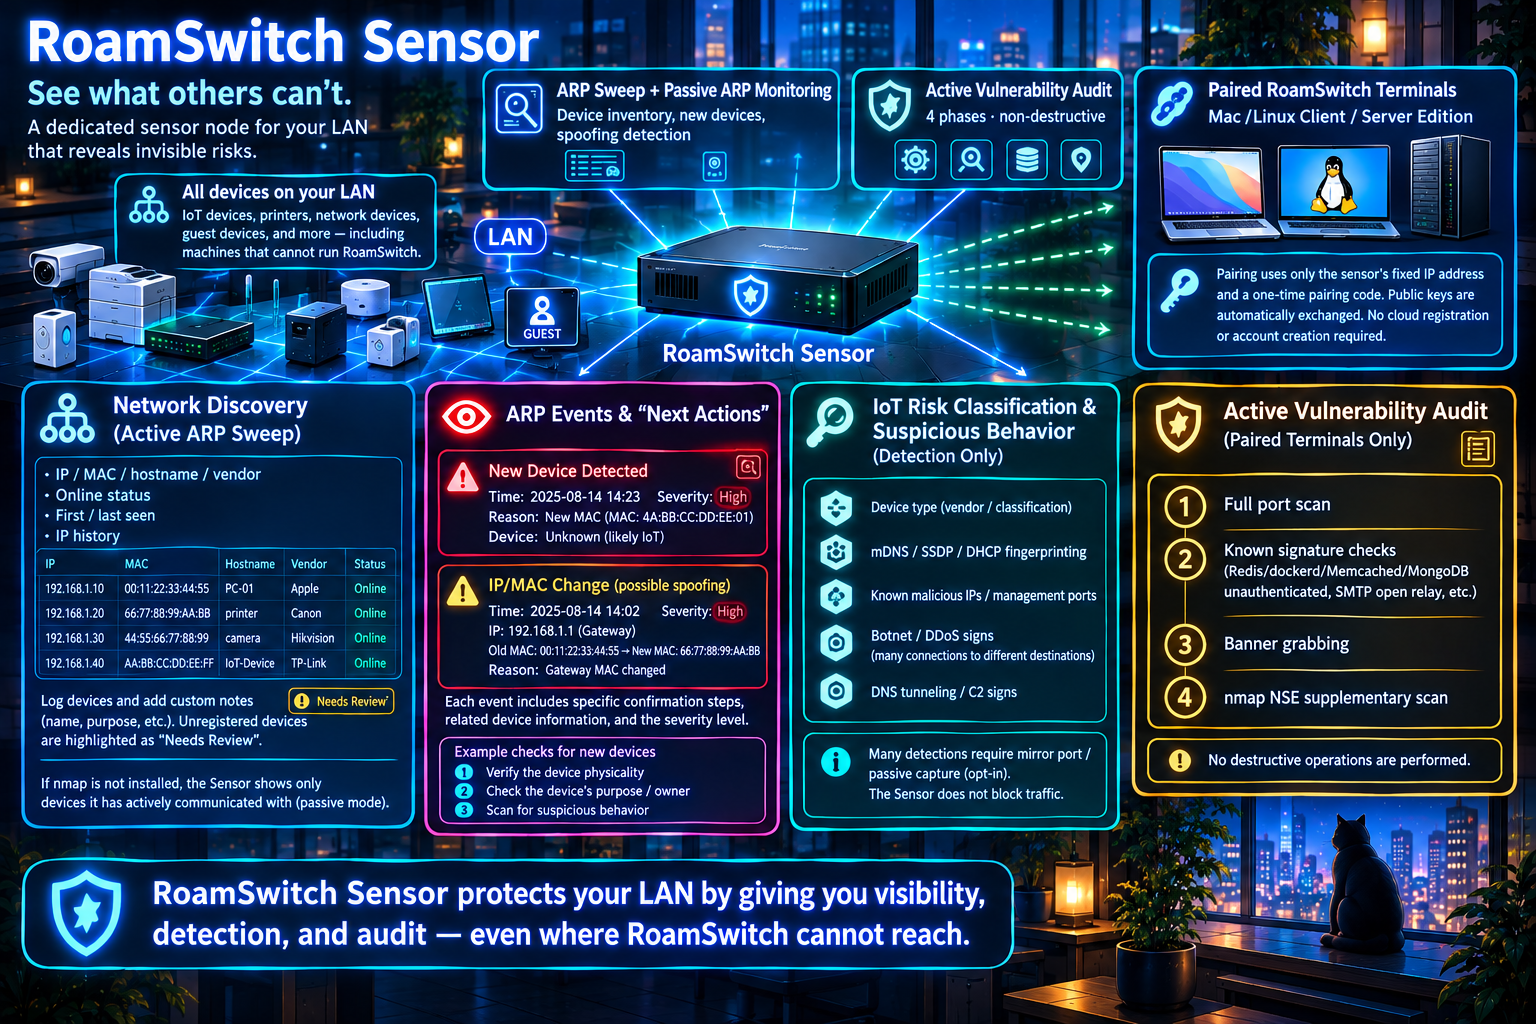
RoamSwitch Sensor는 LAN에 설치하는 전용 노드로, 같은 LAN 상의 RoamSwitch 단말(Mac / Linux Client / Server Edition)을 해당 단말의 외부에서 점검합니다. 호스트 스스로의 자가 진단으로는 원리적으로 볼 수 없는 '같은 LAN의 다른 기기에서 어떻게 보이는가'(열린 포트, 인증 없이 노출된 서비스, 수평 이동의 발판)를 확인합니다. 아울러 LAN 상의 기기 대장과 ARP 스푸핑 감지도 제공합니다.
🛡️ 능동적 취약점 점검(페어링된 단말 대상)
전체 포트 스캔 → 기존 시그니처 점검(Redis/dockerd/Memcached/MongoDB/Elasticsearch/CouchDB/Jenkins/VNC 인증 없는 노출, SMBv1 및 서명 미적용, RDP NLA 미강제, SMTP 오픈 릴레이 등) → 범용 배너 취득 → nmap NSE 보완 점검의 4단계로 구성됩니다. 파괴적인 작업은 전혀 수행하지 않습니다.
📋 네트워크 구성 파악(능동 ARP 스윕)
ARP 스윕으로 LAN 상의 장치를 찾아냅니다. IP・MAC・호스트 이름・제조사・온라인 상태・최초/최근 발견・IP 이력을 장치 목록으로 만들고, 장치마다 이름이나 용도를 자유롭게 기록할 수 있습니다. 메모가 없는 장치는 「확인 필요」로 강조되므로 자산 목록과 대조하는 데 쓸 수 있습니다. nmap이 설치되어 있지 않으면 Sensor가 통신한 장치만 표시하는 수동 모드로 돌아갑니다.
👁️ ARP 이벤트와 「다음에 할 일」
신규 장치의 출현과 알려진 IP에 대한 MAC 변화(ARP 스푸핑의 징후)를 발생 시각・심각도(치명적~정보)・판단 근거・관련 장치의 정체・구체적인 확인 절차와 함께 제시합니다. 게이트웨이 IP의 MAC 변화는 「치명적」으로 다룹니다. 옵트인 수동 캡처를 켜면 한 장치가 많은 IP에 ARP 요청을 보내는 행위(LAN 내 정찰)도 감지합니다.
🔎 LAN 상의 다른 기기 파악과 의심스러운 동작(모두 감지 전용)
MAC 제조사・기기 분류, mDNS/SSDP/DHCP 자기 신고에 의한 모델 식별, 알려진 악성 IP나 관리용 포트로의 접속, 봇넷화・DDoS 가담의 징후(다수의 목적지로 접속), DNS 터널링/C2의 징후를 참고 정보로 제시합니다. 대부분 미러 포트 등 수동 캡처 설정(옵트인)이 필요하며 Sensor가 통신을 차단하는 일은 없습니다.
🔑 페어링 코드 방식(Ed25519・고정 IP)
초기 상태에서는 아무것도 신뢰하지 않습니다. Sensor 운영자가 발급하는 10분간 유효한 1회용 페어링 코드를, 단말 측에서 Sensor의 고정 IP 주소와 함께 입력하면 단 한 번의 조작으로 양방향 신뢰가 성립합니다. 공개 키는 자동으로 교환되므로 사전에 알 필요가 없습니다. 클라우드 등록・계정 생성은 필요하지 않습니다.
📅 정기 감사와 이전 감사와의 차이(옵트인)
페어링된 모든 단말을 정기적으로 자동 감사하고, 이전 감사와의 차이(신규 발견·해소·새로 열린 포트)를 표시합니다. 이전에 열려 있던 포트가 모두 보이지 않게 되면 '해소'가 아니라 '도달 불가 의심'으로 처리합니다. 무인 감사에서도 단말이 마지막으로 인증한 시점의 MAC 주소를 감사 전후에 확인하고, IP 주소가 다른 기기로 넘어갔다면 감사하지 않습니다. 기본값은 꺼져 있으며 실행 간격과 실행 가능 시간대를 설정합니다.
📣 알림과 감사 증적(옵트인)
회귀·신규 기기·ARP 스푸핑 등을 웹훅(Slack·Discord·Teams 등)과 syslog(RFC 5424)로 알릴 수 있습니다. 페어링·해제·감사·설정 변경은 실행자와 함께 변조 감지 기능이 있는 작업 로그(해시 체인)에 기록되며, 감사 결과·기기 대장·작업 로그를 CSV·JSON·HTML 보고서(브라우저에서 PDF로 저장)로 내보낼 수 있습니다. 알림 대상은 모두 운영자가 설정한 곳뿐이며 기본값에서는 아무것도 전송하지 않습니다.
🗂️ 여러 Sensor 집계(중앙 컬렉터, 옵트인)
여러 거점에 Sensor를 두는 조직을 위해 서명된 요약을 수집하는 중앙 컬렉터가 포함되어 있습니다(기본 비활성). 거점별 상태를 확인하는 대시보드와 CSV 내보내기를 제공하며, Sensor 측 감사 로그의 절단·되감기도 감지합니다. 등록한 Sensor의 서명된 요청만 받아들이고, TLS 없이 LAN 밖으로 공개할 수 없습니다.
Sensor 자체에 대한 공격 대책이 필요한 경우, 동일 머신에 RoamSwitch for Linux의 Server Edition을 별도로 설치하는 것을 권장합니다. 두 프로세스는 완전히 독립적으로 공존할 수 있습니다.
감사 보고서 출력 예시
roamswitch-sensor export all --format html(TUI에서는 e 키)로 내보낼 수 있는 보고서의 예시입니다. 단일 HTML 파일이므로 브라우저에서 열어 'PDF로 저장'하면 감사인에게 제출할 수 있는 PDF가 됩니다.
RoamSwitch Sensor 감사 리포트
| 생성 일시 (UTC) | 2026-09-20T02:30:12.508136294+00:00 |
|---|---|
| 거점 | 본사 3층 서버실 |
| Sensor 공개 키 | +kbYCoN5jJSykTAr8zDv/VCs2SdBcrwYbkCrzCRgsLM= |
| 감사 로그 | 무결성 검증: 정상(변조 없음), 18건, head #18 771a265c58fa2f0a8990bc6be79ff5259d96a76a0a3fea472f308df02eaa087f |
단말별 최신 감사 결과
| 단말 | 주소 | 실행 일시 | 발견 | 열린 포트 |
|---|---|---|---|---|
| web-prod-01 | 192.168.20.21 | 2026-09-20T02:00:43.318204577+00:00 | 1건 | 2 |
| db-prod-01 | 192.168.20.22 | 2026-09-20T02:01:14.774390215+00:00 | 2건 | 3 |
| dev-laptop-07 | 192.168.20.35 | 2026-09-20T02:02:07.120765432+00:00 | 문제 없음 | 1 |
발견 사항
| 일시 | 단말 | 포트 | 설명 | 권장 조치 |
|---|---|---|---|---|
| 2026-09-20T02:01:14.774390215+00:00 | db-prod-01 | 22 | SSH 버전 배너 공개 이 SSH 서버는 접속 시 버전 배너를 공개하고 있습니다. 배너 자체는 정상 동작이지만, 공격자가 알려진 취약점을 좁히는 단서가 됩니다. | SSH를 최신 버전으로 업데이트하고, 필요에 따라 배너 내용을 최소화하세요. |
| 2026-09-20T02:01:14.774390215+00:00 | db-prod-01 | 6379 | 알려진 취약점: CVE-2021-32626 (Redis) NVD 설명(영어 원문): Redis is an open source, in-memory database that persists on disk. In affected versions specially crafted Lua scripts executing in Redis can cause the heap-based Lua stack to be overflowed, due to incomplete checks for this condition. This can result with heap corruption and potentially remote code execution. This problem exists in all versions of Redis with Lua scripting support, starting from 2.6. The problem is fixed in versions 6.2.6, 6.0.16 and 5.0.14. | Redis를 CVE-2021-32626의 영향을 받지 않는 버전으로 서둘러 업그레이드하고, 그때까지는 인증 없는 네트워크 접근을 제한하세요. |
| 2026-09-20T02:00:43.318204577+00:00 | web-prod-01 | 22 | SSH 버전 배너 공개 이 SSH 서버는 접속 시 버전 배너를 공개하고 있습니다. 배너 자체는 정상 동작이지만, 공격자가 알려진 취약점을 좁히는 단서가 됩니다. | SSH를 최신 버전으로 업데이트하고, 필요에 따라 배너 내용을 최소화하세요. |
| 2026-09-19T08:33:18.402118906+00:00 | db-prod-01 | 22 | SSH 버전 배너 공개 이 SSH 서버는 접속 시 버전 배너를 공개하고 있습니다. 배너 자체는 정상 동작이지만, 공격자가 알려진 취약점을 좁히는 단서가 됩니다. | SSH를 최신 버전으로 업데이트하고, 필요에 따라 배너 내용을 최소화하세요. |
기기 대장(LAN에서 관측한 모든 기기)
| MAC | IP | 호스트명 | 벤더 | RoamSwitch 관리 | 메모 |
|---|---|---|---|---|---|
| 00:1b:8b:3c:9a:07 | 192.168.20.1 | _gateway | NEC Platforms | 관리 외 | 본사 게이트웨이 라우터 |
| 7c:8b:ca:61:d2:4e | 192.168.20.2 | TP-Link Technologies | 관리 외 | 3층 Wi-Fi 액세스 포인트 | |
| e4:e7:49:2b:70:c1 | 192.168.20.3 | Hewlett Packard | 관리 외 | 2층 복합기 | |
| 90:61:ae:17:4d:e2 | 192.168.20.21 | Intel Corporate | 관리 중 | 운영 웹 서버 | |
| 90:61:ae:17:4d:f9 | 192.168.20.22 | Intel Corporate | 관리 중 | 운영 DB 서버 | |
| 04:20:9a:cc:31:8f | 192.168.20.31 | sensor-hq-01 | Panasonic AVC Networks Company | 관리 외 | RoamSwitch-Sensor |
| a0:c9:a0:5e:83:2b | 192.168.20.35 | Murata Manufacturing | 관리 중 | 개발용 노트북 | |
| 8e:0f:95:a2:64:5d | 192.168.20.44 | 관리 외 | |||
| 5e:e2:59:1d:c8:03 | 192.168.20.45 | 관리 외 | |||
| a8:3b:76:9c:20:e4 | 192.168.20.52 | Cloud Network Technology Singapore PTE. | 관리 외 |
작업 및 승인 로그
| # | 일시 | 실행자 | 작동 | 대상 | 상세 |
|---|---|---|---|---|---|
| 18 | 2026-09-20T02:02:07.120765432+00:00 | scheduler | audit_completed | dev-laptop-07 (Q9mW3sLp0xVc) | trigger=scheduled host=192.168.20.35 findings=0 open_ports=1 new_findings=0 resolved_findings=0 |
| 17 | 2026-09-20T02:02:05.402816653+00:00 | scheduler | audit_started | dev-laptop-07 (Q9mW3sLp0xVc) | host=192.168.20.35 |
| 16 | 2026-09-20T02:01:14.774390215+00:00 | scheduler | audit_completed | db-prod-01 (Zt4Kb8NwY1eR) | trigger=scheduled host=192.168.20.22 findings=2 open_ports=3 new_findings=1 resolved_findings=0 |
| 15 | 2026-09-20T02:01:12.117409552+00:00 | scheduler | audit_started | db-prod-01 (Zt4Kb8NwY1eR) | host=192.168.20.22 |
| 14 | 2026-09-20T02:00:43.318204577+00:00 | scheduler | audit_completed | web-prod-01 (Xk3F9aLm2QzB) | trigger=scheduled host=192.168.20.21 findings=1 open_ports=2 new_findings=1 resolved_findings=0 |
| 13 | 2026-09-20T02:00:41.029385714+00:00 | scheduler | audit_started | web-prod-01 (Xk3F9aLm2QzB) | host=192.168.20.21 |
| 12 | 2026-09-19T09:11:40.318842077+00:00 | cli:uid=1000 | config_changed | schedule.window_end_hour | value=5 |
| 11 | 2026-09-19T09:11:32.640571920+00:00 | cli:uid=1000 | config_changed | schedule.window_start_hour | value=1 |
| 10 | 2026-09-19T09:10:02.205197346+00:00 | cli:uid=1000 | config_changed | schedule.enabled | value=true |
| 9 | 2026-09-19T08:47:19.771263084+00:00 | control_api: | pair | dev-laptop-07 (Q9mW3sLp0xVc) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 8 | 2026-09-19T08:46:52.093718455+00:00 | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 7 | 2026-09-19T08:33:18.402118906+00:00 | cli:uid=1000 | audit_completed | db-prod-01 (Zt4Kb8NwY1eR) | trigger=manual host=192.168.20.22 findings=1 open_ports=2 new_findings=1 resolved_findings=0 |
| 6 | 2026-09-19T08:33:15.588240391+00:00 | cli:uid=1000 | audit_started | db-prod-01 (Zt4Kb8NwY1eR) | manual audit; host=192.168.20.22 |
| 5 | 2026-09-19T08:31:07.336914608+00:00 | control_api: | pair | db-prod-01 (Zt4Kb8NwY1eR) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 4 | 2026-09-19T08:30:41.874526103+00:00 | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 3 | 2026-09-19T08:12:26.152083967+00:00 | control_api: | pair | web-prod-01 (Xk3F9aLm2QzB) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 2 | 2026-09-19T08:11:58.960417225+00:00 | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 1 | 2026-09-19T08:00:03.415602838+00:00 | daemon | daemon_started | version 0.3.4 |
RoamSwitch Sensor Audit Report
| Generated (UTC) | 2026-09-20T02:30:12.508136294+00:00 |
|---|---|
| Site | HQ – 3F server room |
| Sensor public key | +kbYCoN5jJSykTAr8zDv/VCs2SdBcrwYbkCrzCRgsLM= |
| Audit log | Integrity check: OK (no tampering detected) — 18 entries, head #18 771a265c58fa2f0a8990bc6be79ff5259d96a76a0a3fea472f308df02eaa087f |
Latest audit per endpoint
| Endpoint | Address | Timestamp | Findings | Open ports |
|---|---|---|---|---|
| web-prod-01 | 192.168.20.21 | 2026-09-20T02:00:43.318204577+00:00 | 1 finding(s) | 2 |
| db-prod-01 | 192.168.20.22 | 2026-09-20T02:01:14.774390215+00:00 | 2 finding(s) | 3 |
| dev-laptop-07 | 192.168.20.35 | 2026-09-20T02:02:07.120765432+00:00 | clean | 1 |
Findings
| When | Endpoint | Port | Finding | Recommendation |
|---|---|---|---|---|
| 2026-09-20T02:01:14.774390215+00:00 | db-prod-01 | 22 | SSH Version Banner Disclosed This SSH server discloses its version banner on connect. This is normal SSH behavior, but the banner gives an attacker a starting point to look up known vulnerabilities for that version. | Keep SSH updated to the latest version, and minimize the banner's detail if your SSH implementation allows it. |
| 2026-09-20T02:01:14.774390215+00:00 | db-prod-01 | 6379 | Known Vulnerability: CVE-2021-32626 (Redis) Redis is an open source, in-memory database that persists on disk. In affected versions specially crafted Lua scripts executing in Redis can cause the heap-based Lua stack to be overflowed, due to incomplete checks for this condition. This can result with heap corruption and potentially remote code execution. This problem exists in all versions of Redis with Lua scripting support, starting from 2.6. The problem is fixed in versions 6.2.6, 6.0.16 and 5.0.14. | Upgrade Redis to a version not affected by CVE-2021-32626 as soon as possible, and restrict unauthenticated network access to it in the meantime. |
| 2026-09-20T02:00:43.318204577+00:00 | web-prod-01 | 22 | SSH Version Banner Disclosed This SSH server discloses its version banner on connect. This is normal SSH behavior, but the banner gives an attacker a starting point to look up known vulnerabilities for that version. | Keep SSH updated to the latest version, and minimize the banner's detail if your SSH implementation allows it. |
| 2026-09-19T08:33:18.402118906+00:00 | db-prod-01 | 22 | SSH Version Banner Disclosed This SSH server discloses its version banner on connect. This is normal SSH behavior, but the banner gives an attacker a starting point to look up known vulnerabilities for that version. | Keep SSH updated to the latest version, and minimize the banner's detail if your SSH implementation allows it. |
Device inventory (every device observed on the LAN)
| MAC | IP | Hostname | Vendor | Managed | Note |
|---|---|---|---|---|---|
| 00:1b:8b:3c:9a:07 | 192.168.20.1 | _gateway | NEC Platforms | no | HQ gateway router |
| 7c:8b:ca:61:d2:4e | 192.168.20.2 | TP-Link Technologies | no | 3F Wi-Fi access point | |
| e4:e7:49:2b:70:c1 | 192.168.20.3 | Hewlett Packard | no | 2F multifunction printer | |
| 90:61:ae:17:4d:e2 | 192.168.20.21 | Intel Corporate | yes | Production web server | |
| 90:61:ae:17:4d:f9 | 192.168.20.22 | Intel Corporate | yes | Production database server | |
| 04:20:9a:cc:31:8f | 192.168.20.31 | sensor-hq-01 | Panasonic AVC Networks Company | no | RoamSwitch-Sensor |
| a0:c9:a0:5e:83:2b | 192.168.20.35 | Murata Manufacturing | yes | Development laptop | |
| 8e:0f:95:a2:64:5d | 192.168.20.44 | no | |||
| 5e:e2:59:1d:c8:03 | 192.168.20.45 | no | |||
| a8:3b:76:9c:20:e4 | 192.168.20.52 | Cloud Network Technology Singapore PTE. | no |
Operation & approval log
| # | When | Actor | Action | Target | Detail |
|---|---|---|---|---|---|
| 18 | 2026-09-20T02:02:07.120765432+00:00 | scheduler | audit_completed | dev-laptop-07 (Q9mW3sLp0xVc) | trigger=scheduled host=192.168.20.35 findings=0 open_ports=1 new_findings=0 resolved_findings=0 |
| 17 | 2026-09-20T02:02:05.402816653+00:00 | scheduler | audit_started | dev-laptop-07 (Q9mW3sLp0xVc) | host=192.168.20.35 |
| 16 | 2026-09-20T02:01:14.774390215+00:00 | scheduler | audit_completed | db-prod-01 (Zt4Kb8NwY1eR) | trigger=scheduled host=192.168.20.22 findings=2 open_ports=3 new_findings=1 resolved_findings=0 |
| 15 | 2026-09-20T02:01:12.117409552+00:00 | scheduler | audit_started | db-prod-01 (Zt4Kb8NwY1eR) | host=192.168.20.22 |
| 14 | 2026-09-20T02:00:43.318204577+00:00 | scheduler | audit_completed | web-prod-01 (Xk3F9aLm2QzB) | trigger=scheduled host=192.168.20.21 findings=1 open_ports=2 new_findings=1 resolved_findings=0 |
| 13 | 2026-09-20T02:00:41.029385714+00:00 | scheduler | audit_started | web-prod-01 (Xk3F9aLm2QzB) | host=192.168.20.21 |
| 12 | 2026-09-19T09:11:40.318842077+00:00 | cli:uid=1000 | config_changed | schedule.window_end_hour | value=5 |
| 11 | 2026-09-19T09:11:32.640571920+00:00 | cli:uid=1000 | config_changed | schedule.window_start_hour | value=1 |
| 10 | 2026-09-19T09:10:02.205197346+00:00 | cli:uid=1000 | config_changed | schedule.enabled | value=true |
| 9 | 2026-09-19T08:47:19.771263084+00:00 | control_api: | pair | dev-laptop-07 (Q9mW3sLp0xVc) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 8 | 2026-09-19T08:46:52.093718455+00:00 | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 7 | 2026-09-19T08:33:18.402118906+00:00 | cli:uid=1000 | audit_completed | db-prod-01 (Zt4Kb8NwY1eR) | trigger=manual host=192.168.20.22 findings=1 open_ports=2 new_findings=1 resolved_findings=0 |
| 6 | 2026-09-19T08:33:15.588240391+00:00 | cli:uid=1000 | audit_started | db-prod-01 (Zt4Kb8NwY1eR) | manual audit; host=192.168.20.22 |
| 5 | 2026-09-19T08:31:07.336914608+00:00 | control_api: | pair | db-prod-01 (Zt4Kb8NwY1eR) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 4 | 2026-09-19T08:30:41.874526103+00:00 | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 3 | 2026-09-19T08:12:26.152083967+00:00 | control_api: | pair | web-prod-01 (Xk3F9aLm2QzB) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 2 | 2026-09-19T08:11:58.960417225+00:00 | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 1 | 2026-09-19T08:00:03.415602838+00:00 | daemon | daemon_started | version 0.3.4 |
게재된 머신 이름·MAC 주소·IP 주소·공개 키는 모두 가상의 것입니다. 보고서 본문은 일본어 또는 영어로 출력됩니다(일본어 이외의 화면에서는 영어판을 게재합니다).